

PUF-driven Secure Anonymous Authentication Protocol for Internet of Vehicles
-
摘要: 车联网作为智能交通系统的重要组成部分,通过车车与车路信息交互提升交通运行效率,正逐步成为智慧城市建设的重要基础设施。车联网车辆通过周期性广播基本安全消息辅助协同感知与智能决策,但明文传输可能导致车辆身份和行驶轨迹泄露。针对现有匿名认证方案中计算与通信开销较高,以及长期密钥存储易受到物理提取和侧信道攻击等问题,该文提出一种面向车联网的物理不可克隆函数(PUF)驱动安全匿名认证协议。该协议利用集成电路制造过程中形成的随机工艺偏差构建设备相关硬件指纹,并基于PUF激励-响应机制生成会话密钥,结合激励信息构造和更新车辆伪名。该方案利用PUF固有的物理不可克隆特性增强认证安全性,并结合密码学机制实现无需片内存储长期敏感密钥的硬件辅助认证,从而降低物理提取和侧信道攻击导致的密钥泄漏风险。在Dolev–Yao攻击模型下,该文采用BAN逻辑、ProVerif形式化验证和非形式化方法对协议安全性进行分析。分析结果表明,所提方案能够抵御重放攻击、伪装攻击和中间人攻击,并满足匿名性、可追溯性以及协议层身份不可链接性等安全需求。性能分析结果表明,所提方案在保证多项安全功能的同时具有较低的计算与通信开销,适用于资源受限的车联网环境。Abstract:
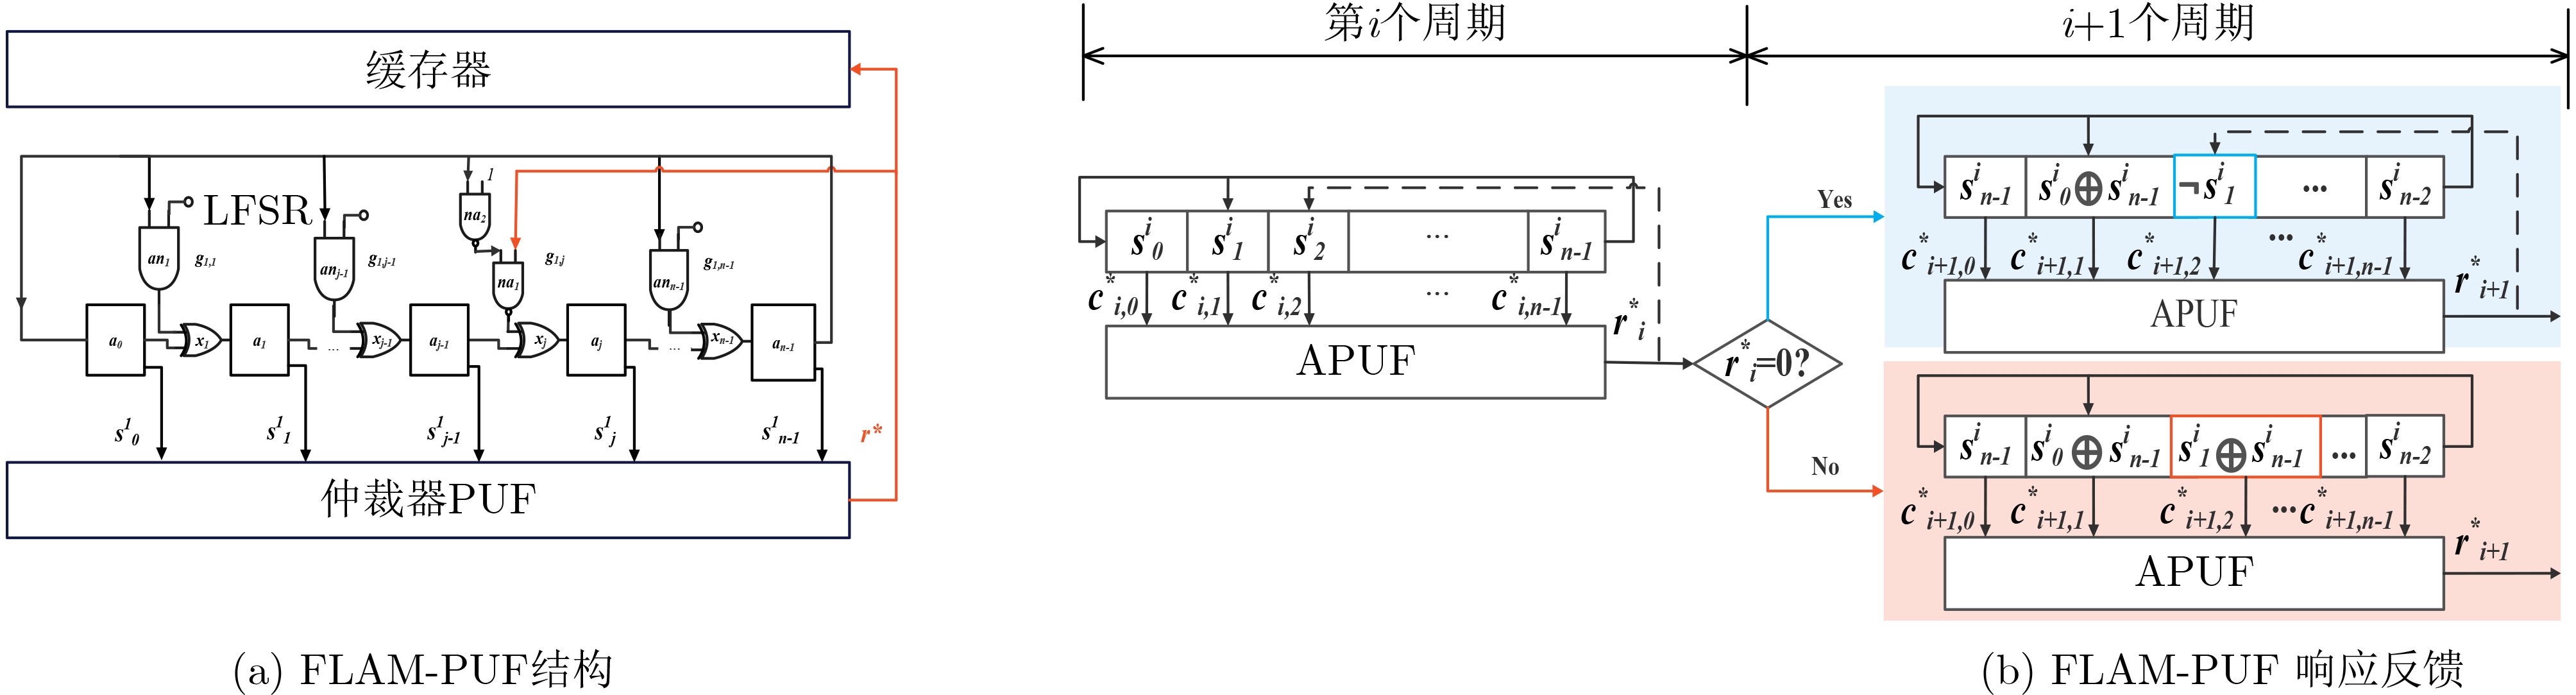
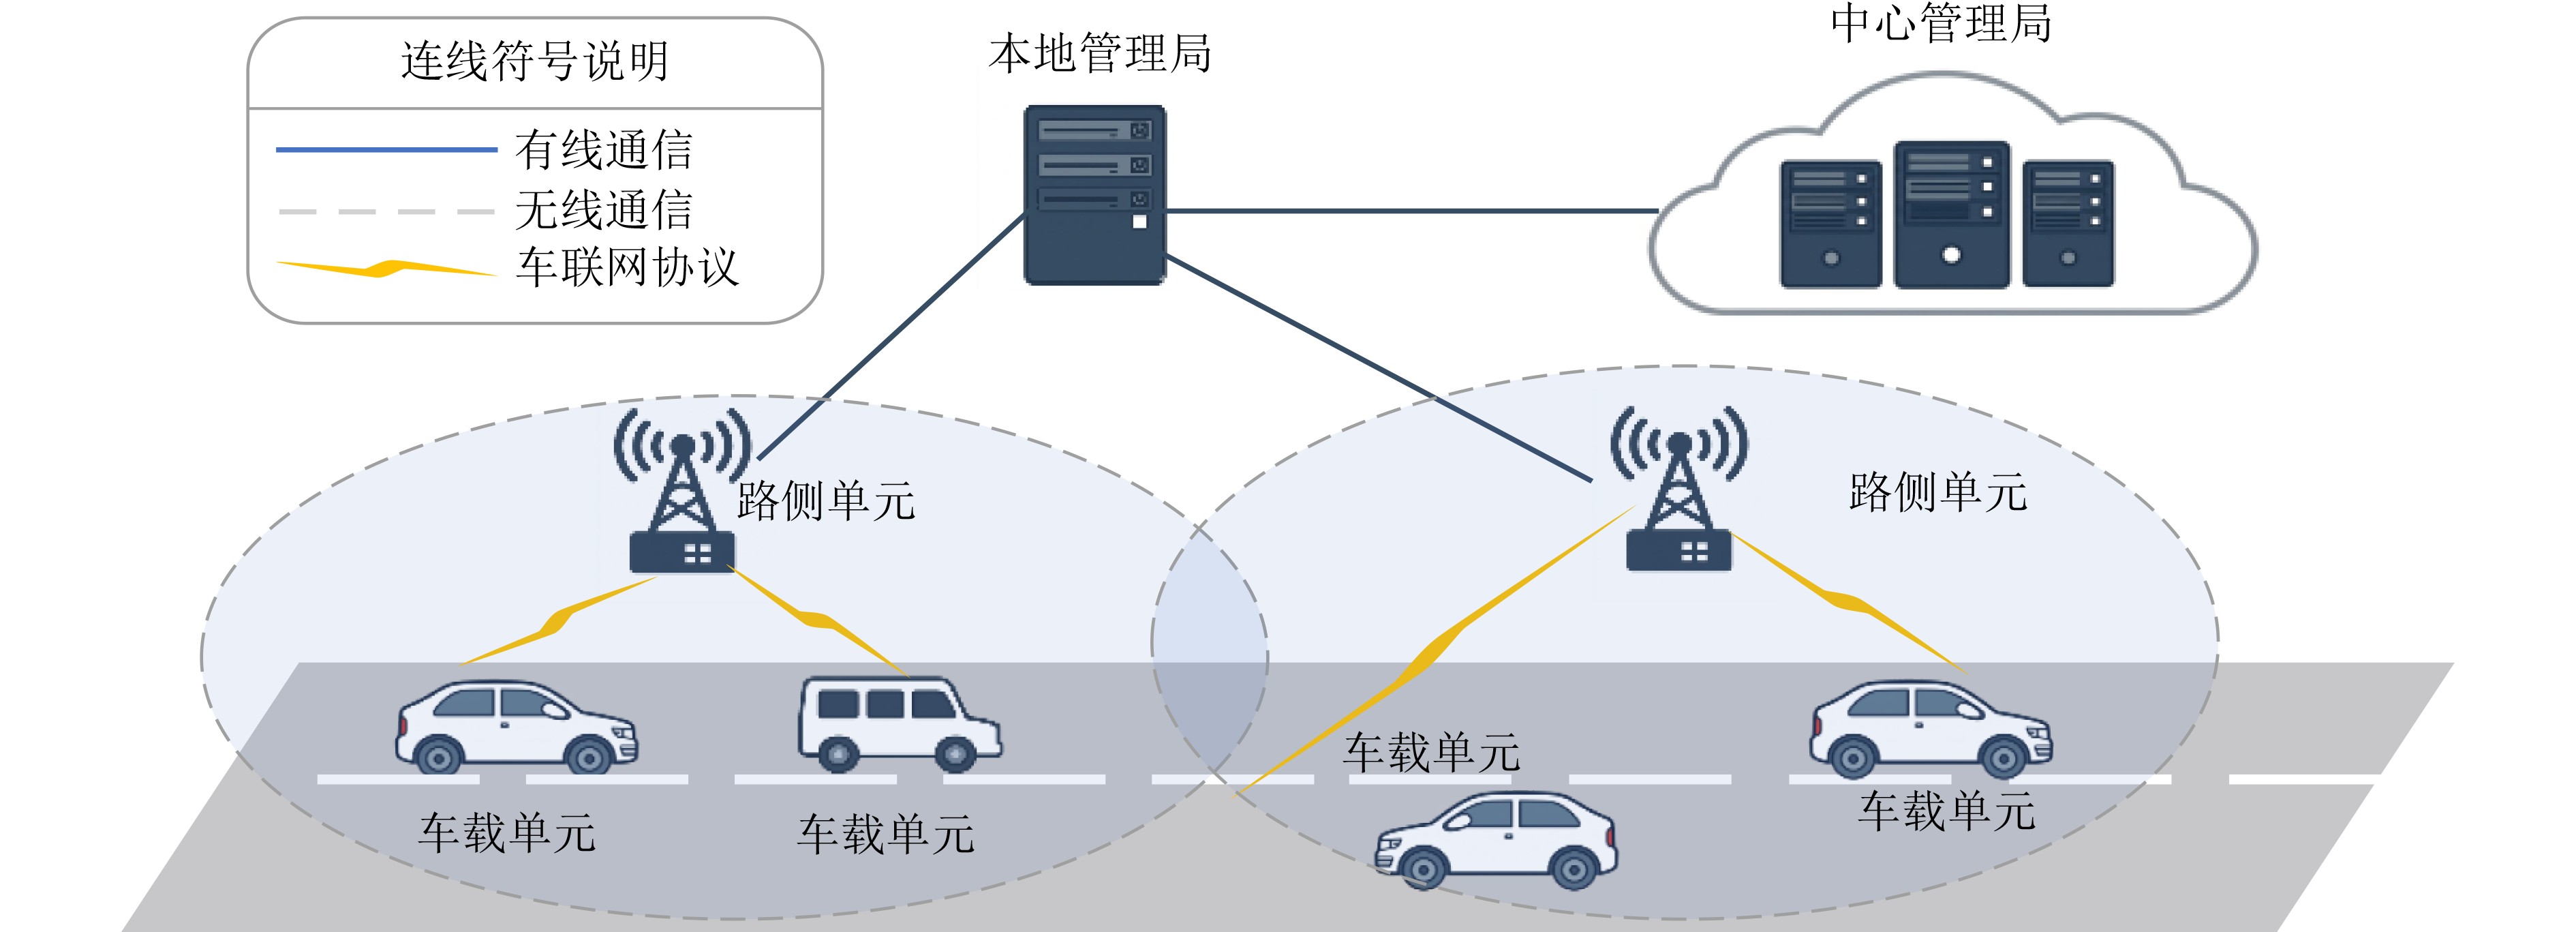
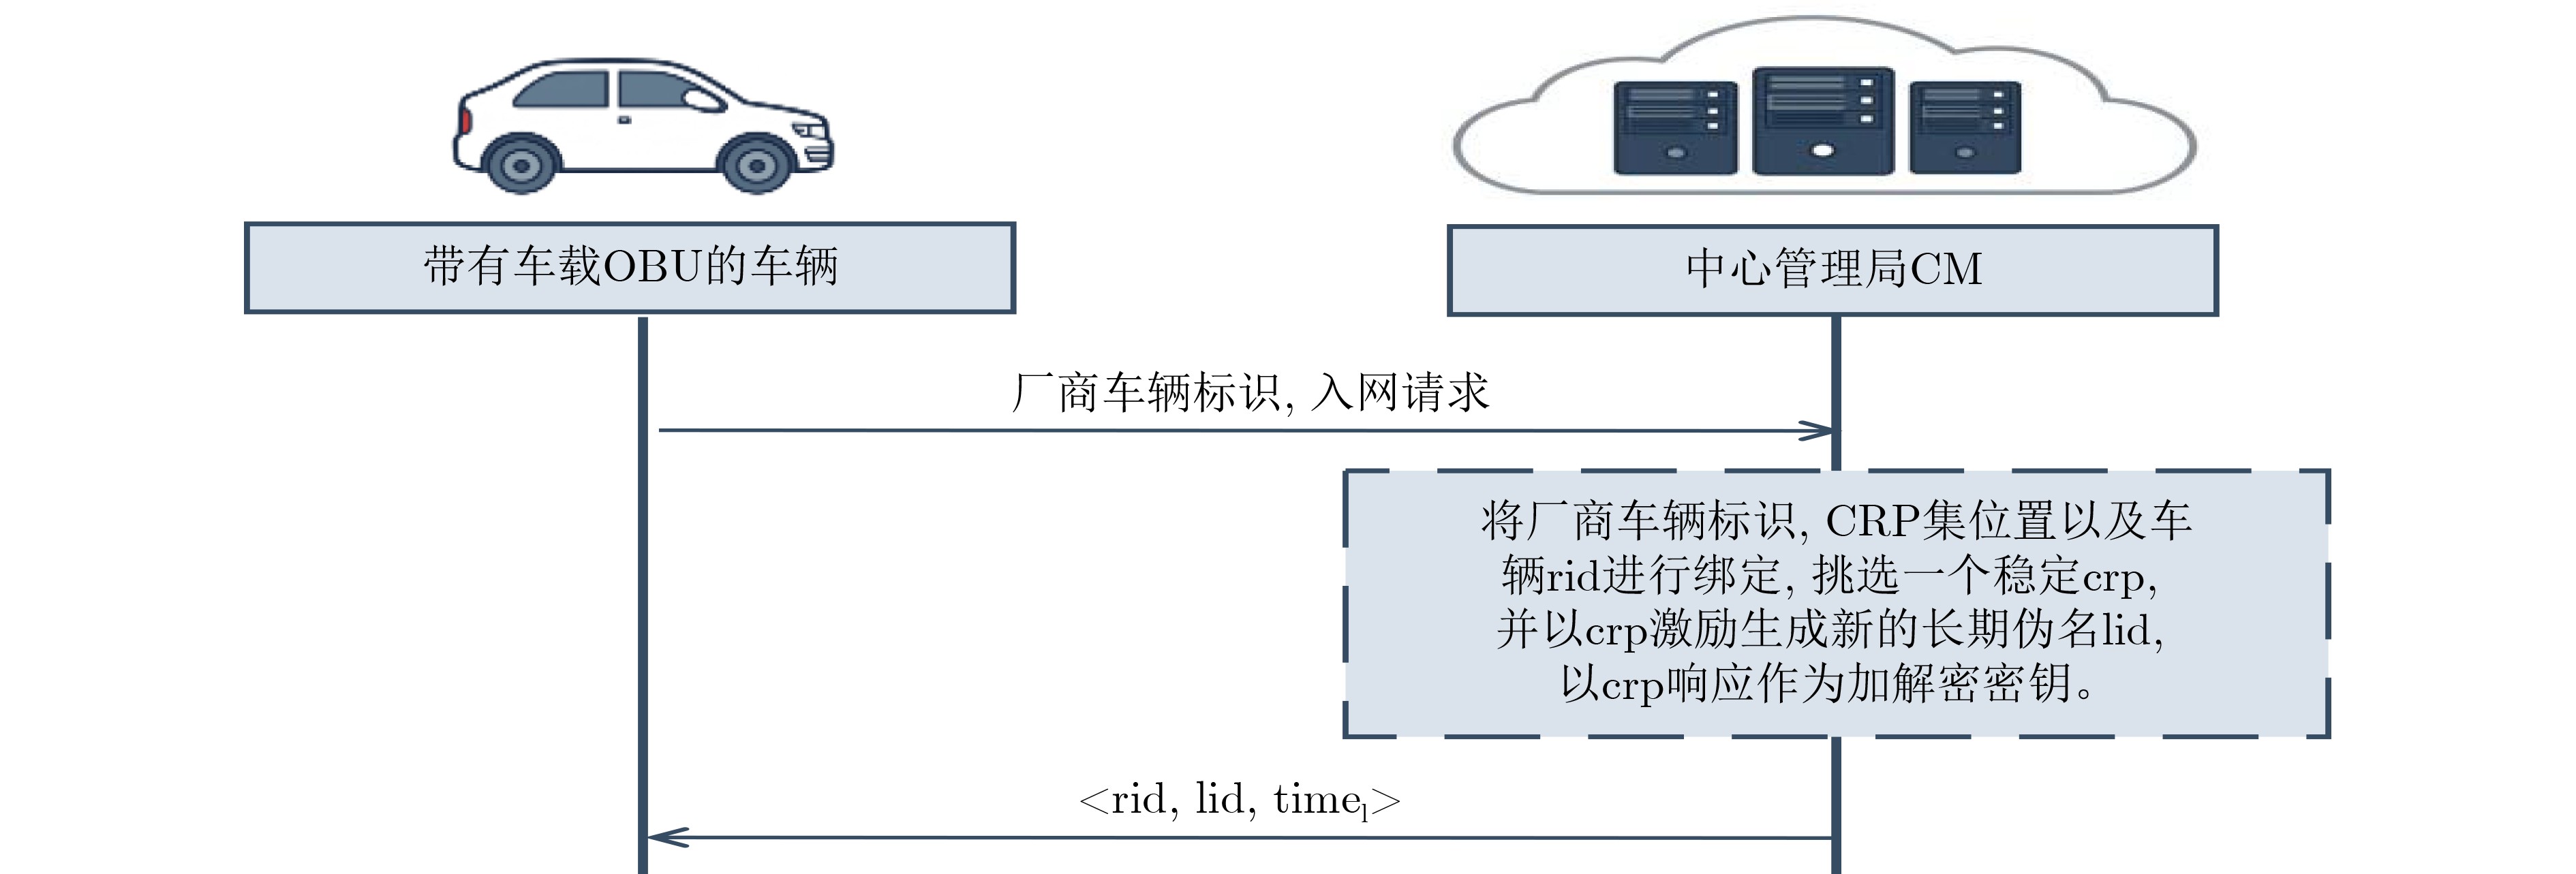
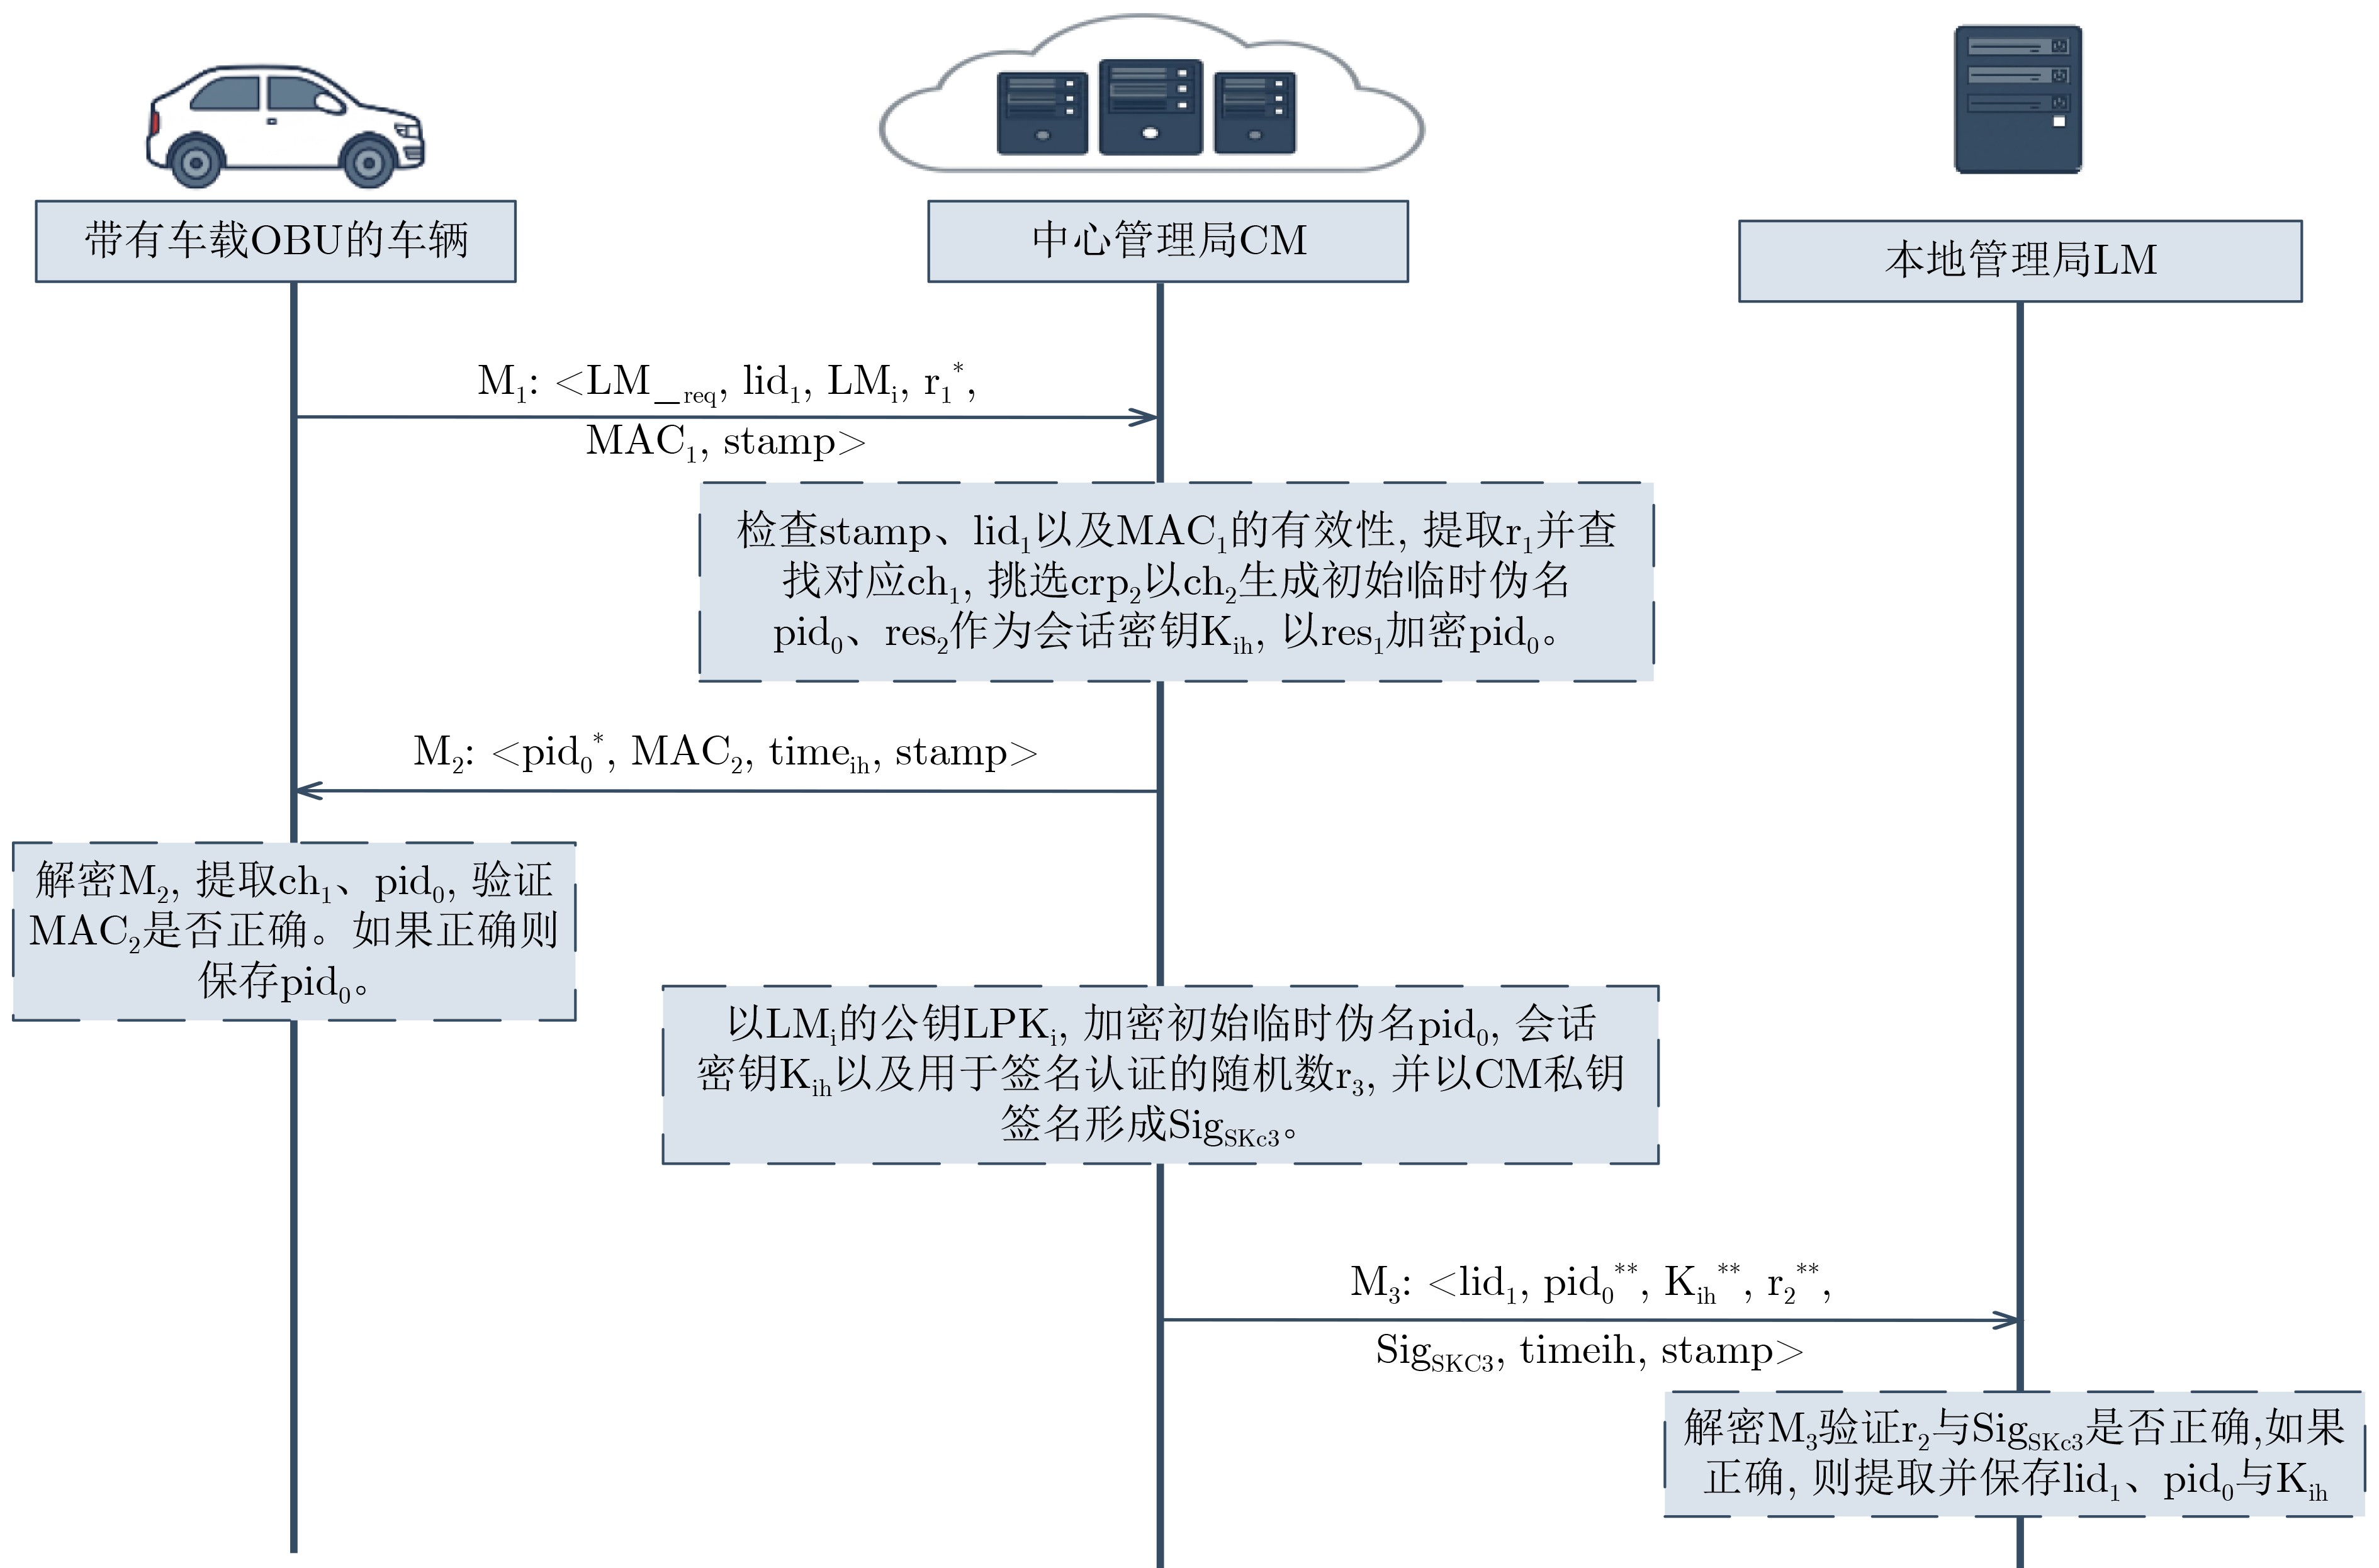
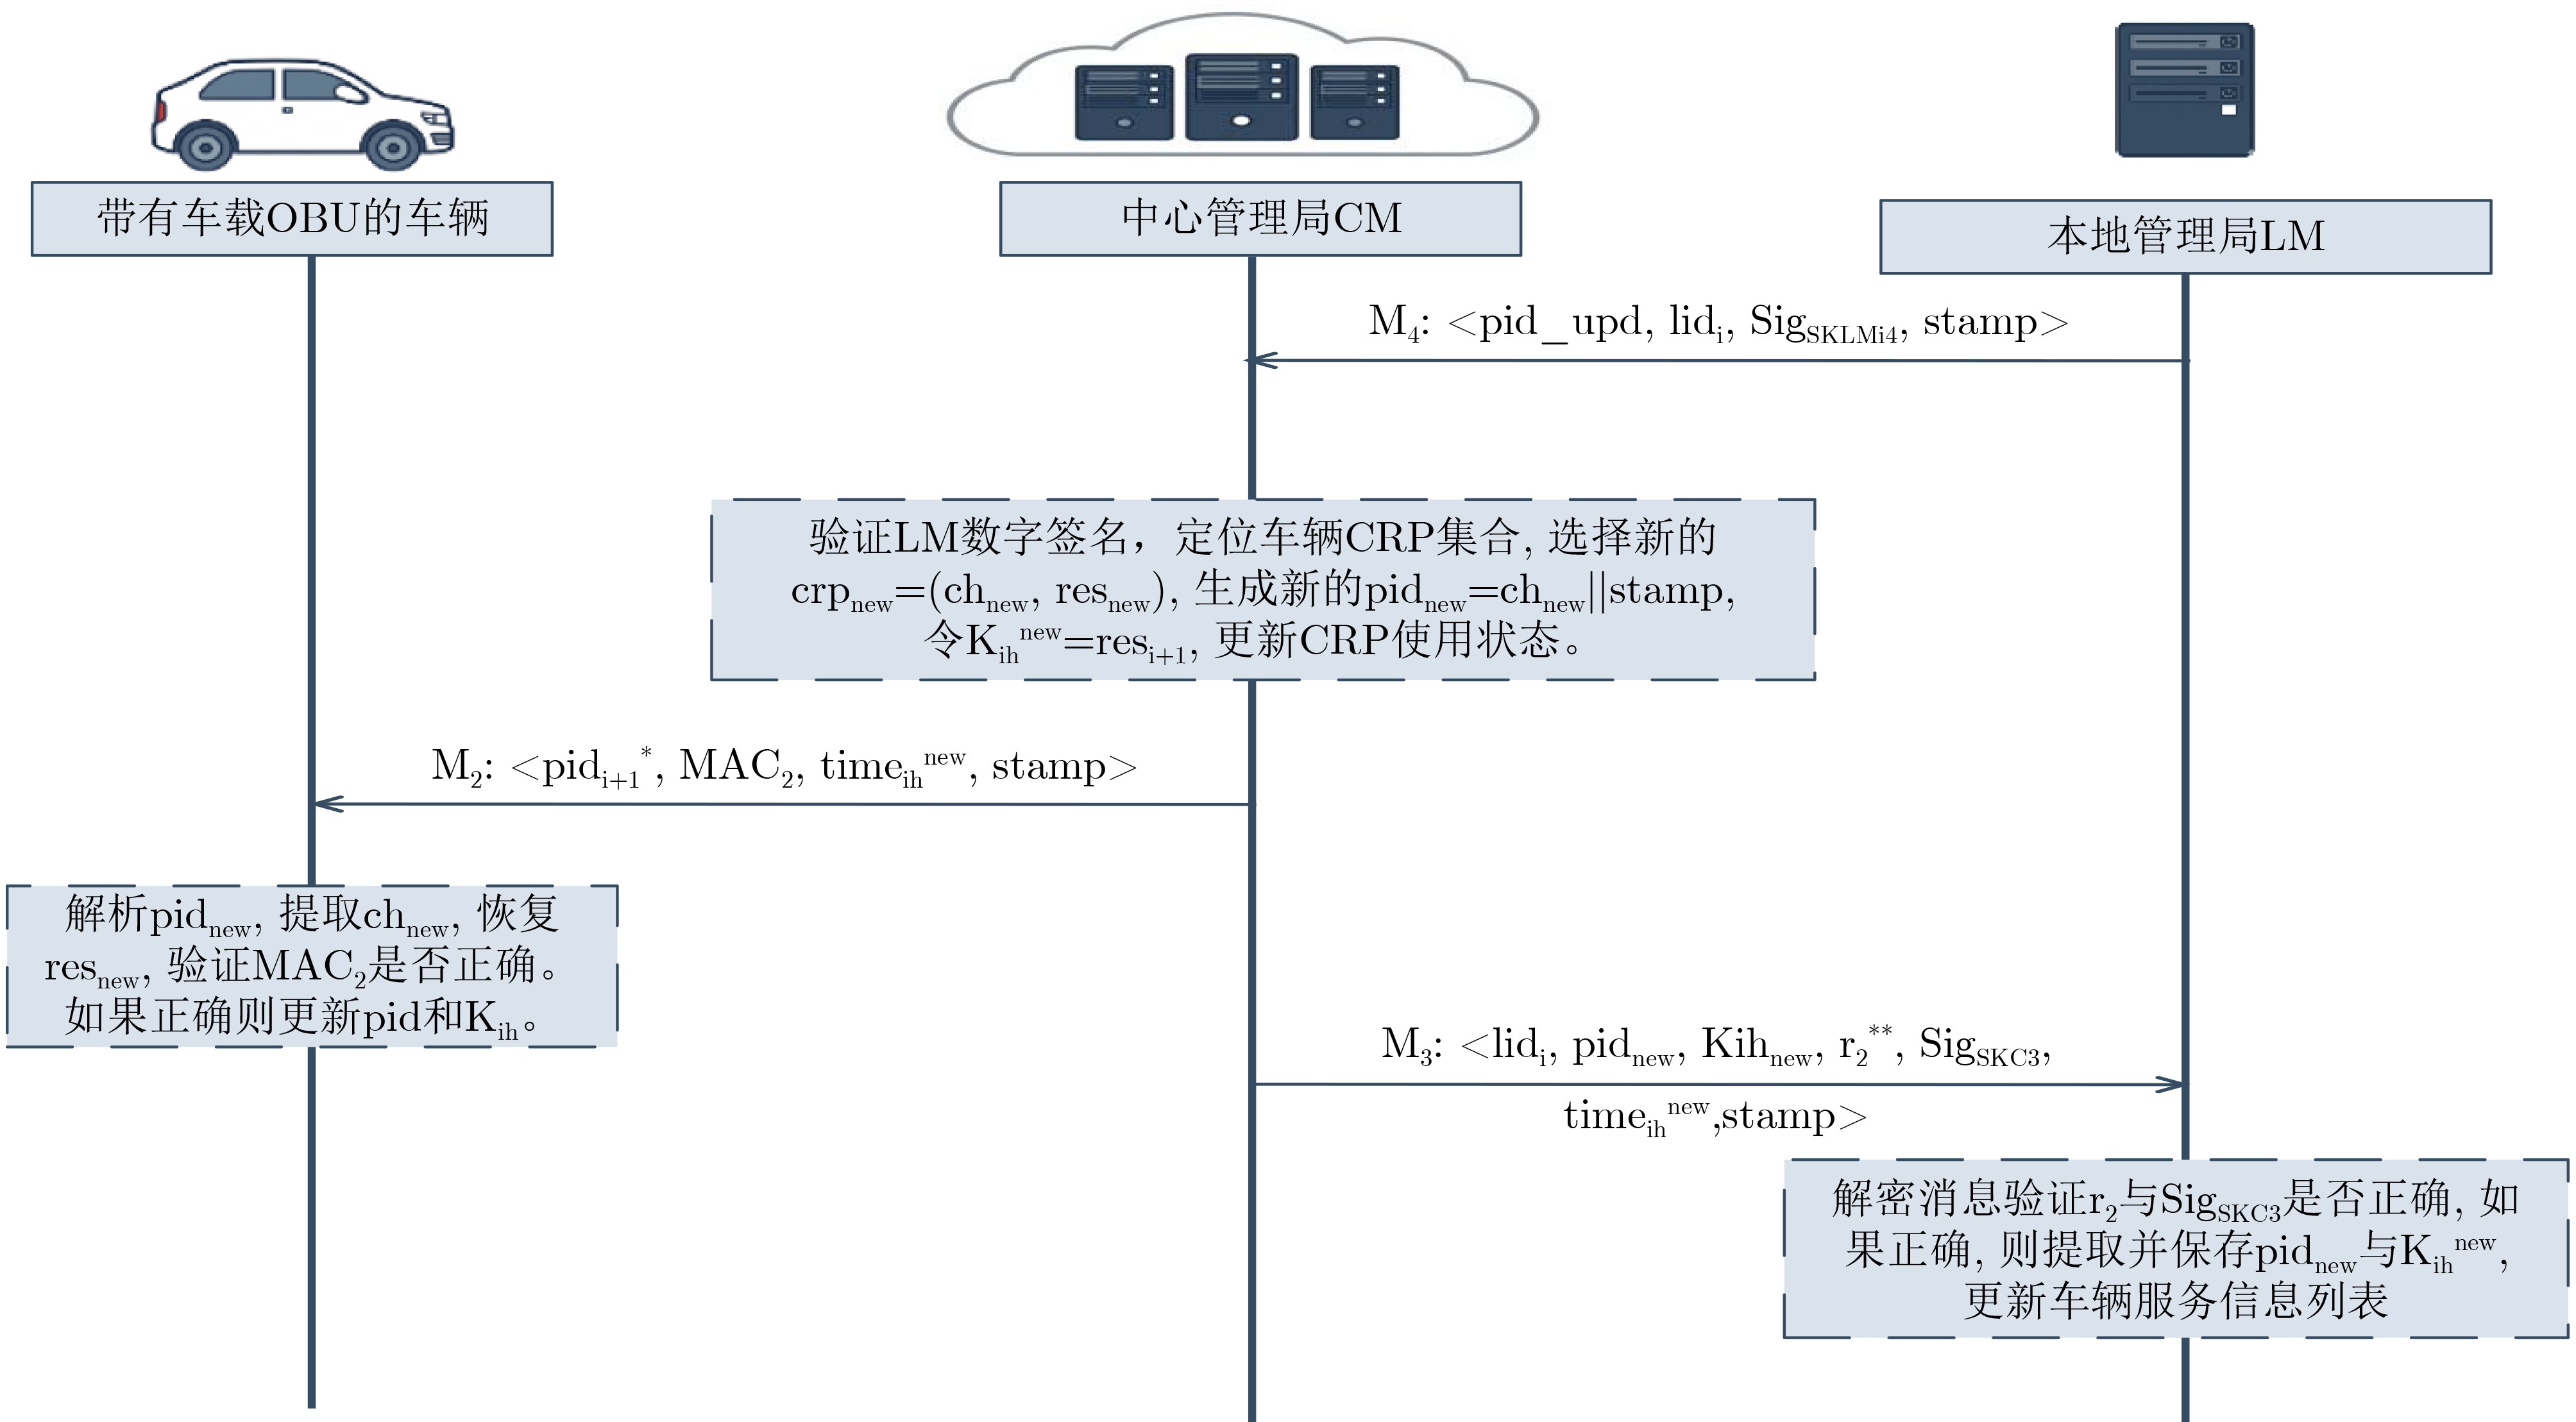
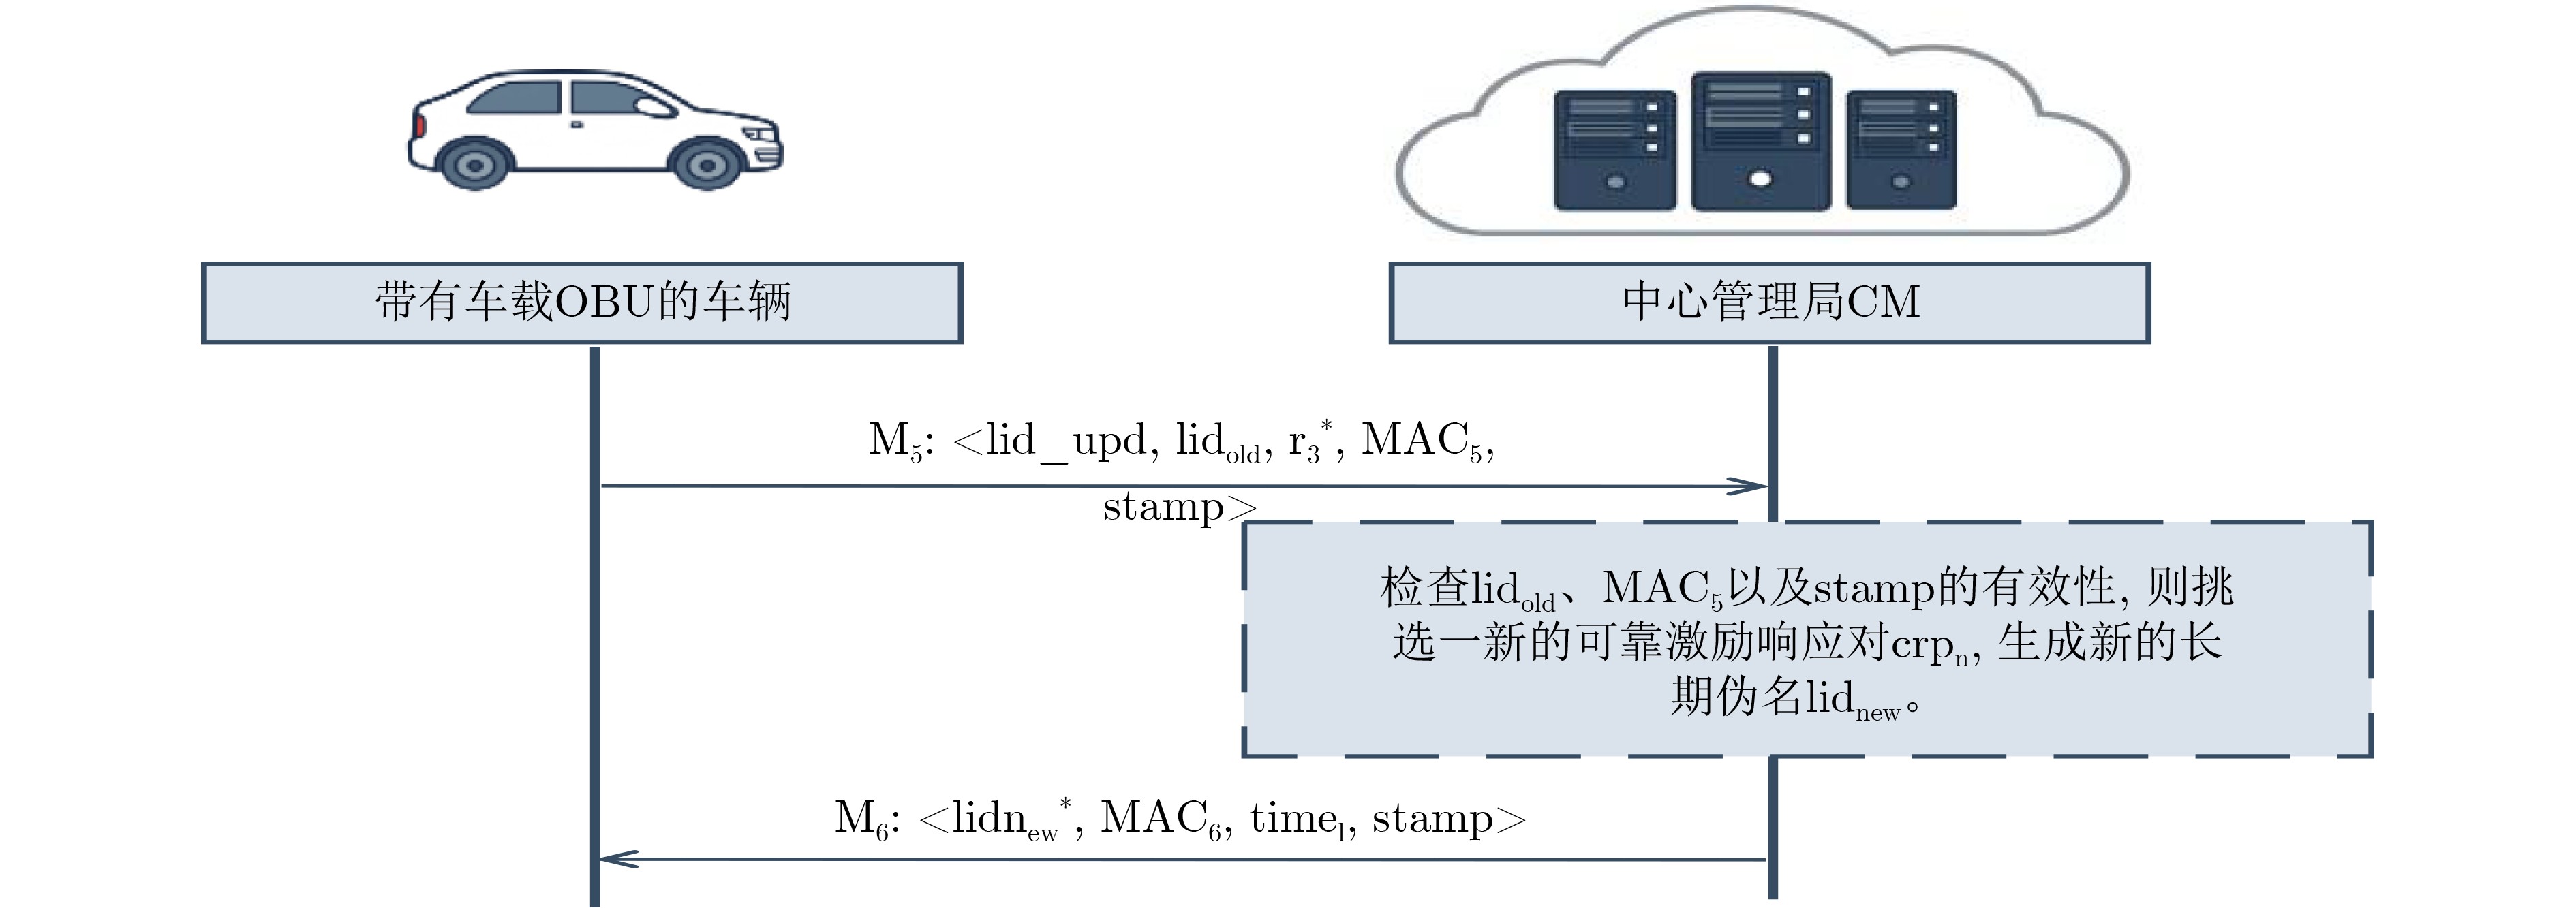
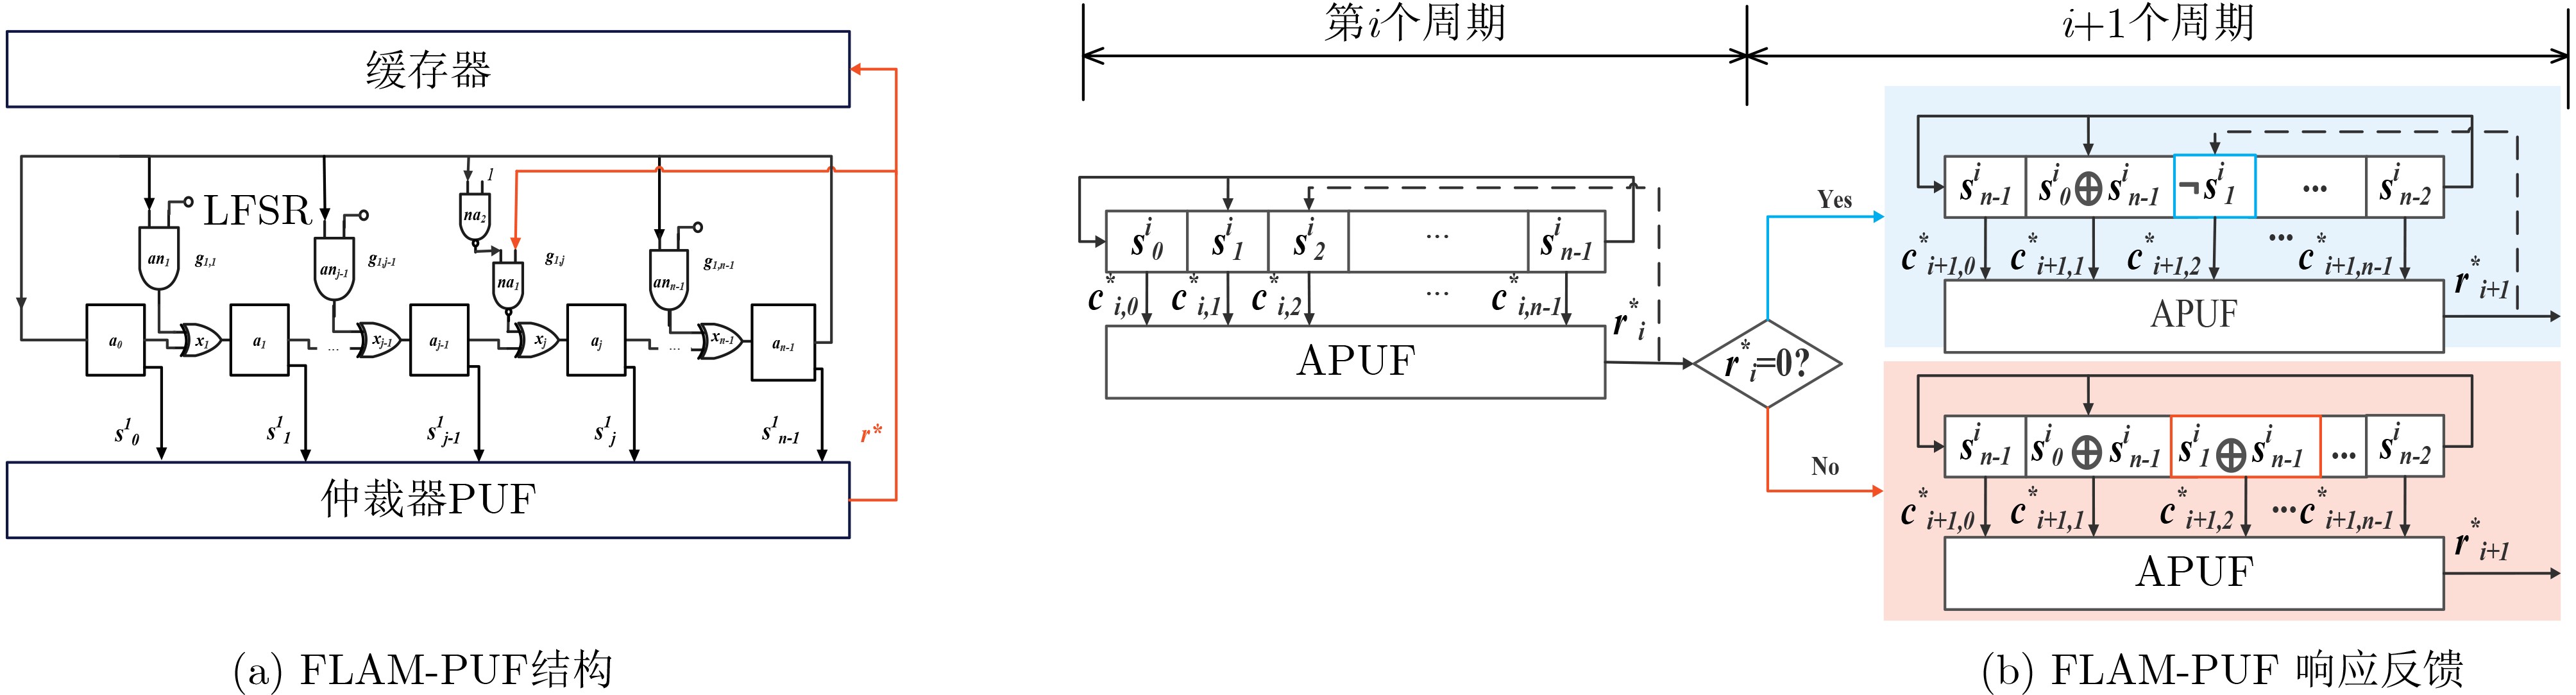
Objective In the Internet of Vehicles (IoV), vehicles often transmit Basic Safety Messages through open wireless links to support road safety and traffic management. However, these messages may expose vehicle identities and travel information. Attackers may collect messages over time and associate them with the same vehicle. Therefore, vehicle authentication should protect both network security and user privacy. Many existing anonymous authentication schemes require complex cryptographic operations, resulting in high computation and communication costs for resource-constrained On-Board Units (OBUs). Some schemes also store long-term secret keys in vehicle devices, which may be exposed through physical extraction or side-channel attacks. A Physical Unclonable Function (PUF) uses random process variations generated during chip fabrication to construct unique hardware features. It can generate device-related responses without directly storing secret keys. Based on this property, this paper proposes a PUF-driven secure anonymous authentication protocol for IoV. The proposed protocol aims to reduce the risk of long-term key storage, protect vehicle identities, and reduce authentication overhead for vehicles. Methods The proposed protocol adopts a response-Feedback-based Lightweight Anti-Machine-learning-attack PUF (FLAM-PUF) as the hardware root of trust. FLAM-PUF combines an Arbiter PUF (APUF) with a reconfigurable Linear Feedback Shift Register (LFSR). The PUF response is fed back to update the LFSR state, which hides the relationship between Challenge–Response Pairs (CRPs) and increases the difficulty of machine-learning modeling attacks ( Fig. 1 ). The system consists of a Center Management (CM), Local Management (LM) entities, Roadside Units (RSUs), and vehicle On-Board Units (OBUs) (Fig. 2 ). During initialization, reliable CRPs are collected in a trusted environment and transmitted to the CM through a secure channel. The main protocol parameters are listed inTable 1 . A PUF challenge is used to generate a vehicle pseudonym, while the corresponding PUF response is used as authentication parameters and session key data. The OBU can recover the required PUF response from its local PUF when needed, eliminating the need to store long-term secret keys. The initialization process is shown inFig. 3 . The protocol adopts two types of pseudonyms. Long-term pseudonyms are used for network access and identity management, while temporary pseudonyms are used for communication within an LM area. The local access process is shown inFig. 4 . Temporary pseudonyms and session keys are updated using unused CRPs (Fig. 5 ), and long-term pseudonyms are renewed before expiration (Fig. 6 ). Security is analyzed under the Dolev–Yao model using Burrows–Abadi–Needham (BAN) logic, ProVerif formal verification, and informal security analysis.Results and Discussions The proposed protocol combines PUF-based key generation with dynamic pseudonym management. First, FLAM-PUF uses response feedback and a reconfigurable LFSR to hide the internal CRP relationship, increasing the difficulty of machine-learning modeling attacks ( Fig. 1 ). Second, the use of long-term and temporary pseudonyms separates network access from local vehicle communication. CRPs, pseudonyms, and session keys are updated synchronously, reducing the possibility that attackers associate vehicle identities across different authentication periods (Fig. 4 ,Fig. 5 , andFig. 6 ). BAN logic analysis shows that the vehicle can verify the binding between the temporary pseudonym and the PUF-based session key, while the LM can verify that this binding is authorized by the CM. ProVerif verification results show that the secrecy queries for vehicle identities and PUF responses are satisfied, and all three injective authentication correspondences hold. Under the assumed freshness and one-time CRP usage conditions, the results support the protocol's resistance to replay and impersonation attacks. Informal security analysis demonstrates that the protocol provides mutual authentication, anonymity, traceability, revocability, and protocol-level identity unlinkability. It also resists replay, impersonation, man-in-the-middle, and false message attacks (Table 3 ). In addition, the OBU does not need to store long-term secret keys in nonvolatile memory because the required PUF responses can be recovered when needed, reducing the risk of direct key extraction. For performance evaluation, the execution times of the main cryptographic operations are measured (Table 4 ), and the computation costs of the OBU, CM, and LM at each protocol stage are summarized in Table 5. For one complete online authentication and session key agreement process, the computation time of the proposed scheme on the OBU is approximately 1 365.99 ms, and the communication cost is 992 bits (Table 6 ). Under the same evaluation conditions, its computation time is close to that of Ref. [14 ] and lower than those of Refs. [15 ]–[17 ]. Its communication cost is lower than those of all four compared schemes. These results demonstrate that the proposed protocol provides more security functions while maintaining low vehicle-side costs.Conclusions This paper proposes a PUF-driven secure anonymous authentication protocol for IoV. FLAM-PUF is used as a hardware root of trust to recover authentication parameters and session key data when needed, avoiding direct storage of long-term secret keys in OBUs. The combination of long-term and temporary pseudonyms supports anonymous access, identity tracing, revocation, and protocol-level identity unlinkability. BAN logic, ProVerif formal verification, and informal security analysis show that the proposed protocol satisfies its main security requirements and resists common network attacks. Performance evaluation results show that one online authentication and session key agreement process requires approximately 1 365.99 ms of OBU computation and 992 bits of communication ( Table 6 ). The proposed protocol achieves a balance among security, privacy protection, and low computational cost, making it suitable for resource-constrained IoV devices. -
表 1 伪名管理方案参数表
符号 描述 符号 描述 Vh 第h辆车 PKc 中心管理局CM公钥 CM 中心管理局 SKc 中心管理局CM私钥 LMi 第i个本地管理局 CRP PUF的激励响应对集合 RSU 路侧单元 crpx 第x个激励响应对 rid 车辆全网唯一永久标识 chx crpx的激励 lid 车辆长期伪名 resx crpx的响应 pid 车辆临时伪名 Enckey{} 以key为密钥的加密操作 Kch 车辆Vh与中心管理局CM之间基于PUF响应建立的认证密钥 Deckey{} 以key为密钥的解密操作 Kih 车辆Vh与本地管理局LMi之间的共享会话密钥 stamp 时间戳 LPK 本地管理局LM公钥 r 随机数 LSK 本地管理局LM私钥 time 伪名或者密钥使用有效期  下载: 导出CSV
表 2 ProVerif安全查询及验证结果
验证目标 ProVerif查询/对应关系 验证结果 永久身份机密性 query attacker(rid) 成立 当前PUF响应及
认证密钥机密性query attacker(res1) 成立 新PUF响应及会话
密钥机密性query attacker(res2) 成立 CM对车辆的认证 CM接受$\Rightarrow $车辆发起 注入对应关系成立 车辆对CM的认证 车辆接受$\Rightarrow $CM生成M2 注入对应关系成立 LMi对CM的认证 LM接受$\Rightarrow $CM生成
并签署M3注入对应关系成立
下载: 导出CSV
表 4 密码学操作运行时间
符号 定义 运行时间(μs) 符号 定义 运行时间(μs) TP 物理不可克隆函数(PUF) 682 TAD 非对称解密 25282 Th 哈希函数 0.172 TEM 椭圆曲线点乘 1996 TE 对称加密 0.947 TEA 椭圆曲线点加 85.486 TD 对称解密 0.699 TX 按位异或 9.38 TSig RSA数字签名生成 2183.71 TVer RSA数字签名验证 410.09 TAE 非对称加密 27122 TF 模糊提取 493.63
下载: 导出CSV
表 5 各阶段各实体计算运行情况
认证阶段 计算实体 计算开销 本地入网请求 车辆OBU 2TP+2Th+TE+TD 中心管理局CM 2Th+2TE+TD+3TAE+TSig 本地管理局LM 3TAD+TVer 临时伪名更新 车辆OBU TP+TD+Th 中心管理局CM TVer+Th+TE+TAE+TSig 本地管理局LM TVer+TAE+TSig 长期伪名更新 车辆OBU 2TP+2Th+TE+TD 中心管理局CM 2Th+TE+TD
下载: 导出CSV
-
[1] CVE. 特斯拉车载通信控制单元(TCU)认证绕过漏洞[EB/OL]. https://cve.imfht.com/detail/CVE-2025-34251, 2026. CVE. Tesla Telematics Control Unit (TCU) Authentication Bypass Vulnerability[EB/OL]. https://cve.imfht.com/detail/CVE-2025-34251, 2026. [2] 张晓均, 唐浩宇, 张楠, 等. 分布式智能车载网联系统的匿名认证与密钥协商协议[J]. 电子与信息学报, 2024, 46(4): 1333–1342. doi: 10.11999/JEIT230394.ZHANG Xiaojun, TANG Haoyu, ZHANG Nan, et al. Anonymous authentication and key agreement protocol based on distributed intelligent vehicle networking system[J]. Journal of Electronics & Information Technology, 2024, 46(4): 1333–1342. doi: 10.11999/JEIT230394. [3] 张应辉, 李国腾, 韩刚, 等. 5G车联网中安全高效的组播服务认证与密钥协商方案[J]. 电子与信息学报, 2024, 46(7): 3026–3035. doi: 10.11999/JEIT231118.ZHANG Yinghui, LI Guoteng, HAN Gang, et al. Secure and efficient authentication and key agreement scheme for multicast services in 5G vehicular to everything[J]. Journal of Electronics & Information Technology, 2024, 46(7): 3026–3035. doi: 10.11999/JEIT231118. [4] MANASRAH A, YASEEN Q, AL-AQRABI H, et al. Identity-based authentication in VANETs: A review[J]. IEEE Transactions on Intelligent Transportation Systems, 2025, 26(4): 4260–4282. doi: 10.1109/TITS.2025.3528932. [5] VERMA G K, RANA S, TIWARI A, et al. Dynamic anonymous hierarchical edge-assisted batch verifiable authentication for VANETs[J]. IEEE Transactions on Vehicular Technology, 2025, 74(9): 14735–14744. doi: 10.1109/TVT.2025.3566415. [6] WANG Yahui, JIA Xiaoying, BAO Yingying, et al. Efficient and provably secure offline/online heterogeneous signcryption scheme for VANETs[J]. IEEE Internet of Things Journal, 2024, 11(24): 41248–41260. doi: 10.1109/JIOT.2024.3458077. [7] LI Kang, AU M H, HO W H, et al. An efficient conditional privacy-preserving authentication scheme for vehicular ad hoc networks using online/offline certificateless aggregate signature[C]. The 13th International Conference on Provable Security, Cairns, Australia, 2019: 59–76. doi: 10.1007/978-3-030-31919-9_4. [8] ZHOU Ziyu, WANG Pengjun, LI Gang, et al. Improving the stability of APUF to 100% without extra hardware overhead for enhancing the performance of security authentication protocols[J]. IEEE Internet of Things Journal, 2025, 12(12): 19818–19832. doi: 10.1109/JIOT.2025.3541434. [9] NI Li, WU Siyuan, PU Jinwei, et al. Highly reliable RRAM-based physical unclonable function with auto-write technique[J]. IEEE Transactions on Very Large Scale Integration (VLSI) Systems, 2026, 34(6): 2000–2004. doi: 10.1109/TVLSI.2026.3670888. [10] WU Linjun, HU Yupeng, ZHANG Kehuan, et al. FLAM-PUF: A response–feedback-based lightweight anti-machine-learning-attack PUF[J]. IEEE Transactions on Computer-Aided Design of Integrated Circuits and Systems, 2022, 41(11): 4433–4444. doi: 10.1109/TCAD.2022.3197696. [11] CHOI J, KWON D, SON S, et al. A PUF-based lightweight authentication scheme for UAV-assisted internet of vehicles[J]. IEEE Transactions on Intelligent Transportation Systems, 2025, 26(9): 13782–13798. doi: 10.1109/TITS.2025.3564581. [12] JIA Chunzhi, TAN Weijie, SHEN Ao, et al. A PUF-enhanced fog-enabled hierarchical authentication protocol for internet of vehicles[J]. IEEE Internet of Things Journal, 2025, 12(18): 37629–37644. doi: 10.1109/JIOT.2025.3583822. [13] SHEN Ao, TAN Weijie, JIA Chunzhi, et al. CUBE-PUF-based anonymous mutual authentication protocol for internet of vehicles[J]. IEEE Internet of Things Journal, 2025, 12(18): 38697–38709. doi: 10.1109/JIOT.2025.3586869. [14] LI Jiping, CHEN Jing, LIU Yining, et al. An efficient and revocable PUF-based authentication scheme for secure V2R mutual communication in VANETs[J]. IEEE Internet of Things Journal, 2025, 12(18): 37974–37987. doi: 10.1109/JIOT.2025.3585643. [15] 夏卓群, 苏潮, 徐梓桑, 等. 基于物理不可克隆函数的轻量级可证明安全车联网认证协议[J]. 电子与信息学报, 2024, 46(9): 3788–3796. doi: 10.11999/JEIT240141.XIA Zhuoqun, SU Chao, XU Zisang, et al. A lightweight and provably secure authentication protocol for internet of vehicles using physical unclonable function[J]. Journal of Electronics & Information Technology, 2024, 46(9): 3788–3796. doi: 10.11999/JEIT240141. [16] VIJAYAKUMAR P, RAJASEKARAN A S, AZEES M, et al. Probably secure PUF-based anonymous mutual and batch authentication for inter-vehicular communications in VANET[J]. IEEE Transactions on Vehicular Technology, 2026, 75(2): 2516–2526. doi: 10.1109/TVT.2025.3600097. [17] YANG Yuting, TAN Weijie, LI Zhen, et al. Mutual authentication protocols based on PUF and multitrusted authority for internet of vehicles[J]. IEEE Internet of Things Journal, 2024, 11(24): 40086–40099. doi: 10.1109/JIOT.2024.3449901. [18] CHAUHDARY S H, MA Tengfei, JIANG Linhua, et al. PUF-ILM: A PUF-enabled authentication scheme for internet of vehicles using improved logical mapping[J]. IEEE Internet of Things Journal, 2026, 13(7): 13787–13800. doi: 10.1109/JIOT.2026.3656432. [19] ZHOU Ziyu, LI Gang, ZHANG Yuejun, et al. A strong PUF-based security protocol to protect AI model parameters against privacy information leakage[J]. IEEE Internet of Things Journal, 2025, 12(12): 20815–20827. doi: 10.1109/JIOT.2025.3544555. [20] XIE Yuanfeng, JIANG Weiwei, LUO Hanqing, et al. A lightweight and efficient authentication protocol based on AST PUF and Schnorr for IoT[J]. IEEE Internet of Things Journal, 2026, 13(1): 1606–1621. doi: 10.1109/JIOT.2025.3629693. [21] DOLEV D and YAO A. On the security of public key protocols[J]. IEEE Transactions on Information Theory, 1983, 29(2): 198–208. doi: 10.1109/TIT.1983.1056650. [22] BLANCHET B. An efficient cryptographic protocol verifier based on Prolog rules[C]. The 14th IEEE Computer Security Foundations Workshop, Cape Breton, Canada, 2001: 82–96. doi: 10.1109/CSFW.2001.930138. -

 下载:

图(6) / 表(6)
计量
- 文章访问数: 312
- HTML全文浏览量: 71
- PDF下载量: 15
- 被引次数: 0
