

A Behavioral Economics-Based Game Model for Side-Channel Security Attack and Defense Strategies
-
摘要: 为解决侧信道安全领域暂无系统化攻防策略选择模型的现状,该文通过引入行为经济学和层次分析法,构建了一种侧信道攻防策略结构化成本量化模型。首先,从博弈论基本要素出发,将侧信道分析者与防护设计者映射为博弈双方,建立策略空间与收益函数。随后,提出基于层次分析法的成本量化框架,通过构建多维度判断矩阵,系统量化攻防策略的客观成本,克服传统主观赋值法的随意性与不可复现性。在此基础上,创新性地引入前景理论和风险规避理论,建立不完全信息静态博弈模型,并采用贝叶斯-纳什均衡求解最优策略。进一步结合安全工程ALARP原则,提出安全等级依赖的动态决策模型。结果表明,该模型能够为不同安全等级的场景提供基于风险偏好和成本效益原则量化的策略选择指导,明确识别出资产价值与防护强度的非线性临界关系,有效实现防护强度与资产价值的自适应匹配。通过构建“心理-经济-工程”三重维度的决策框架,不仅为侧信道攻防策略选择提供了首个系统化、可复现的理论模型,也为密码模块的“适度安全”设计提供了跨学科的量化决策依据。Abstract:
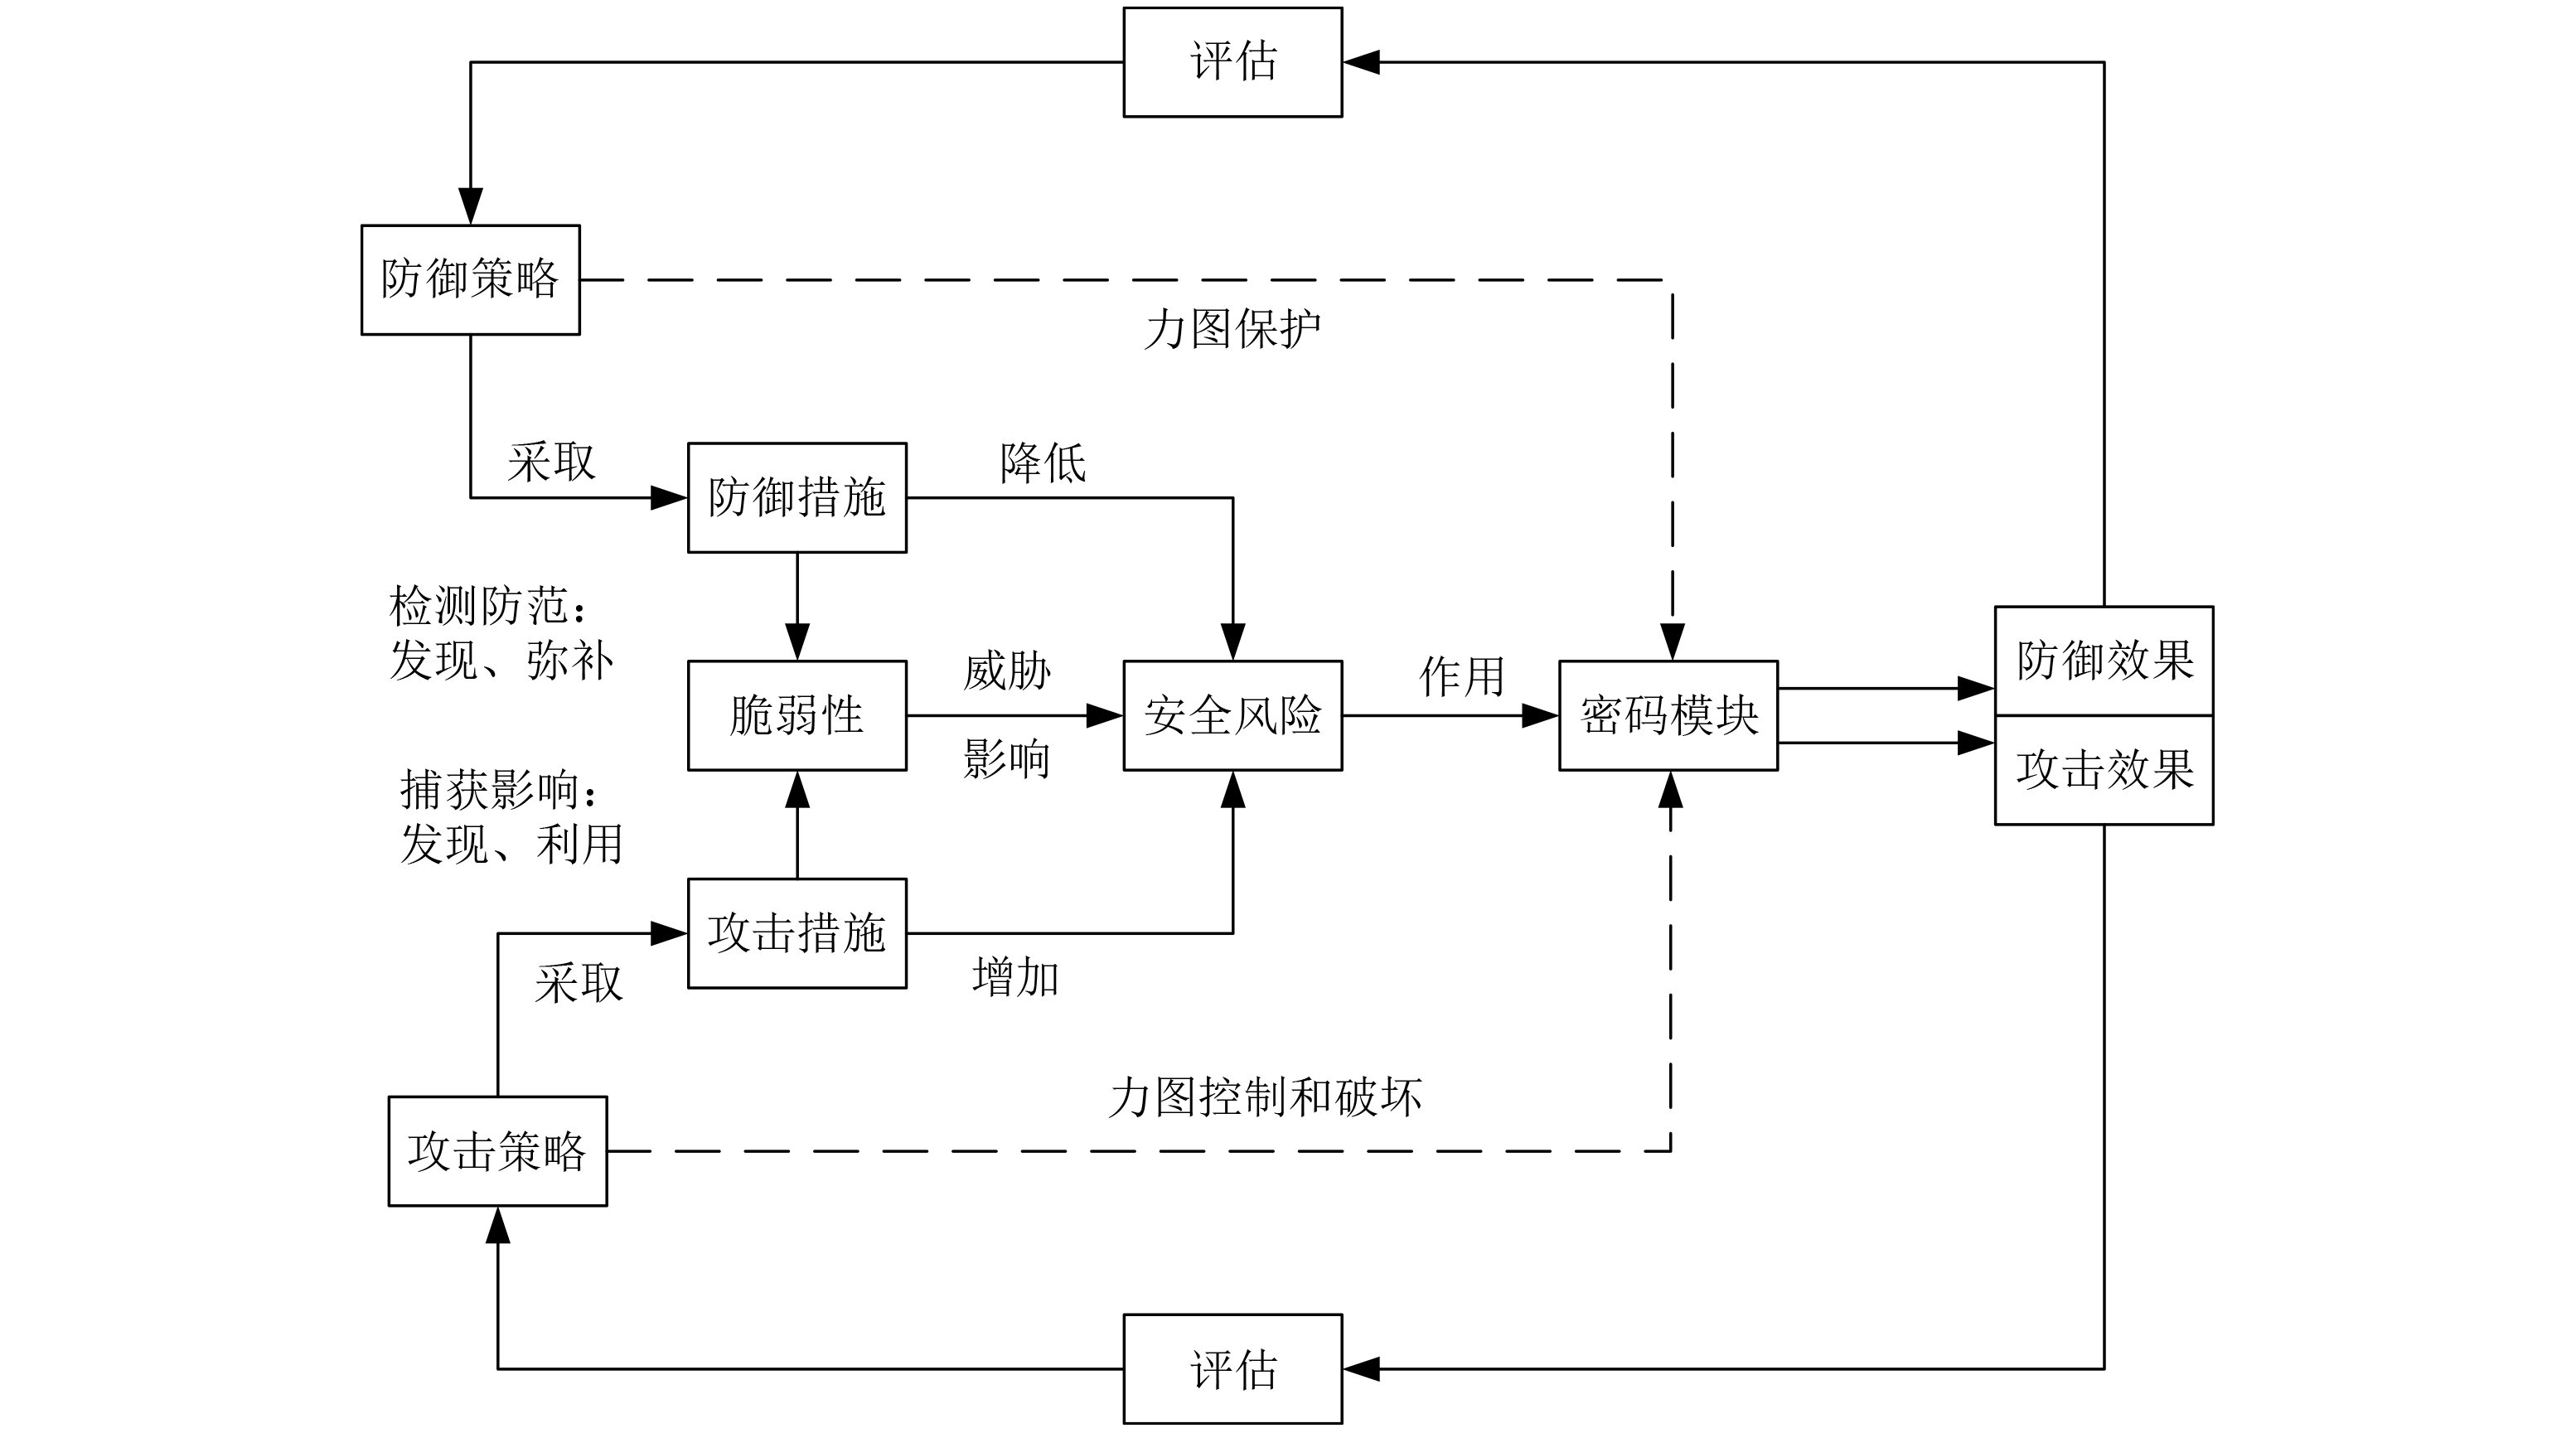
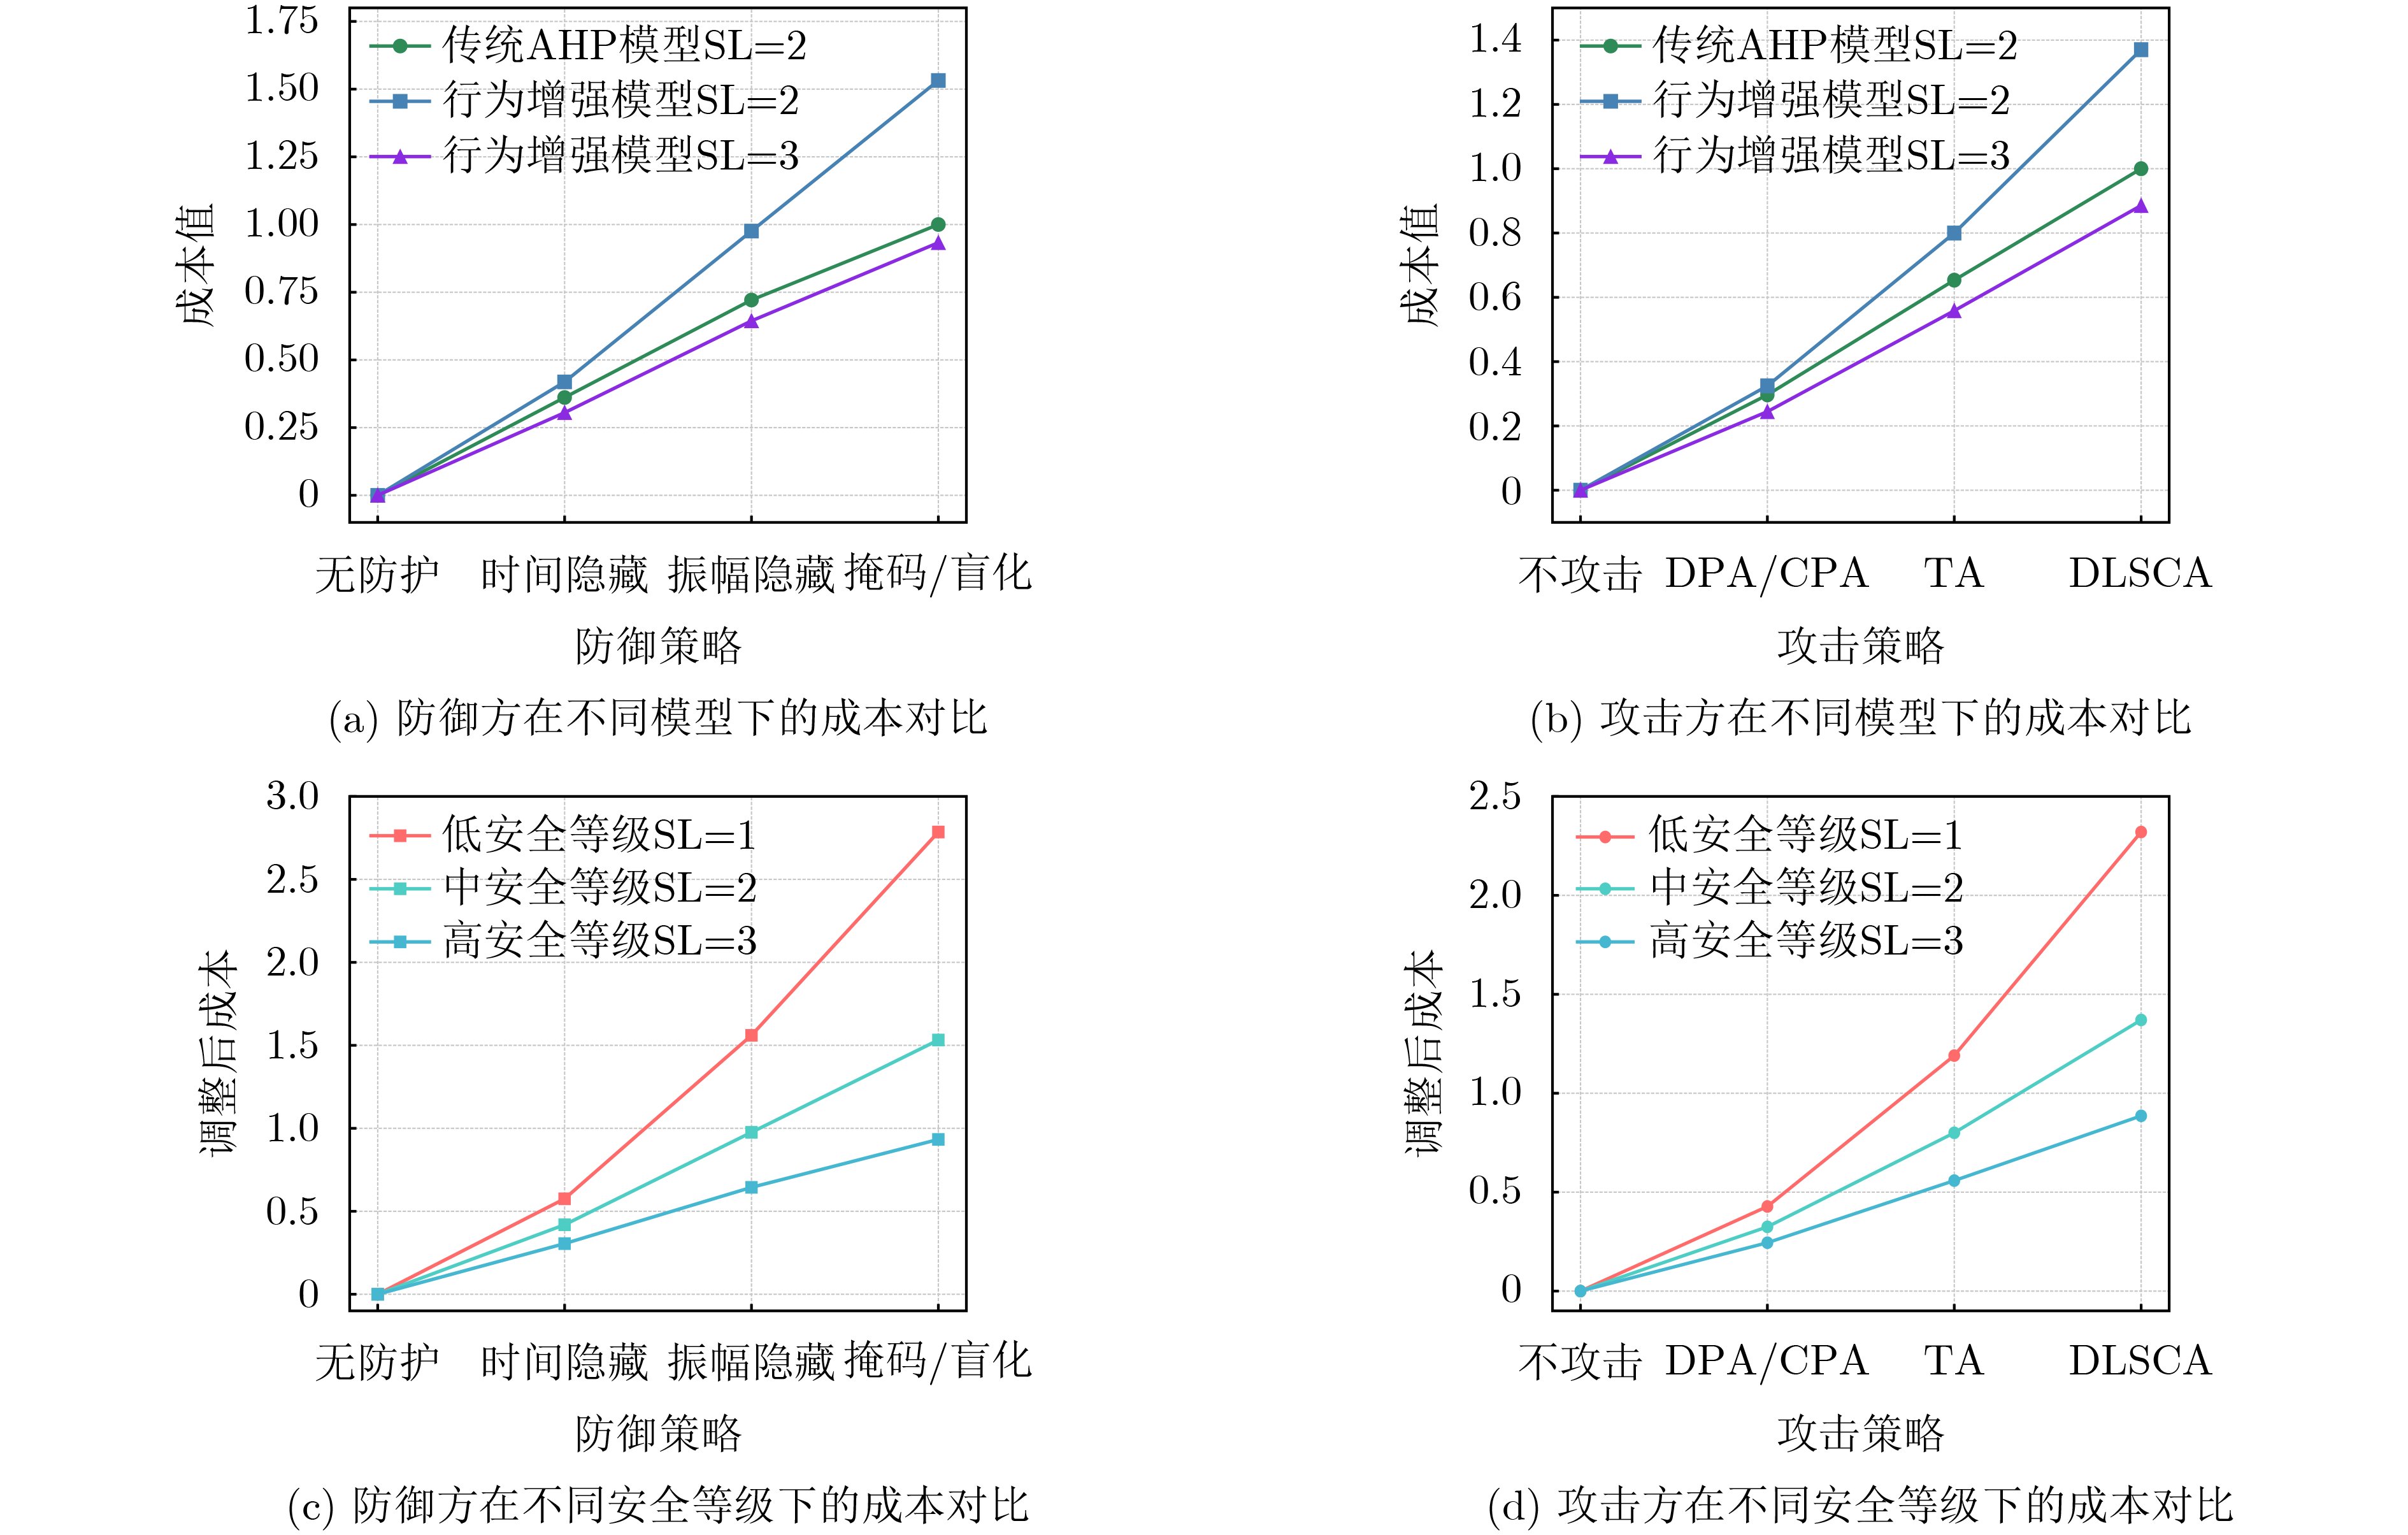
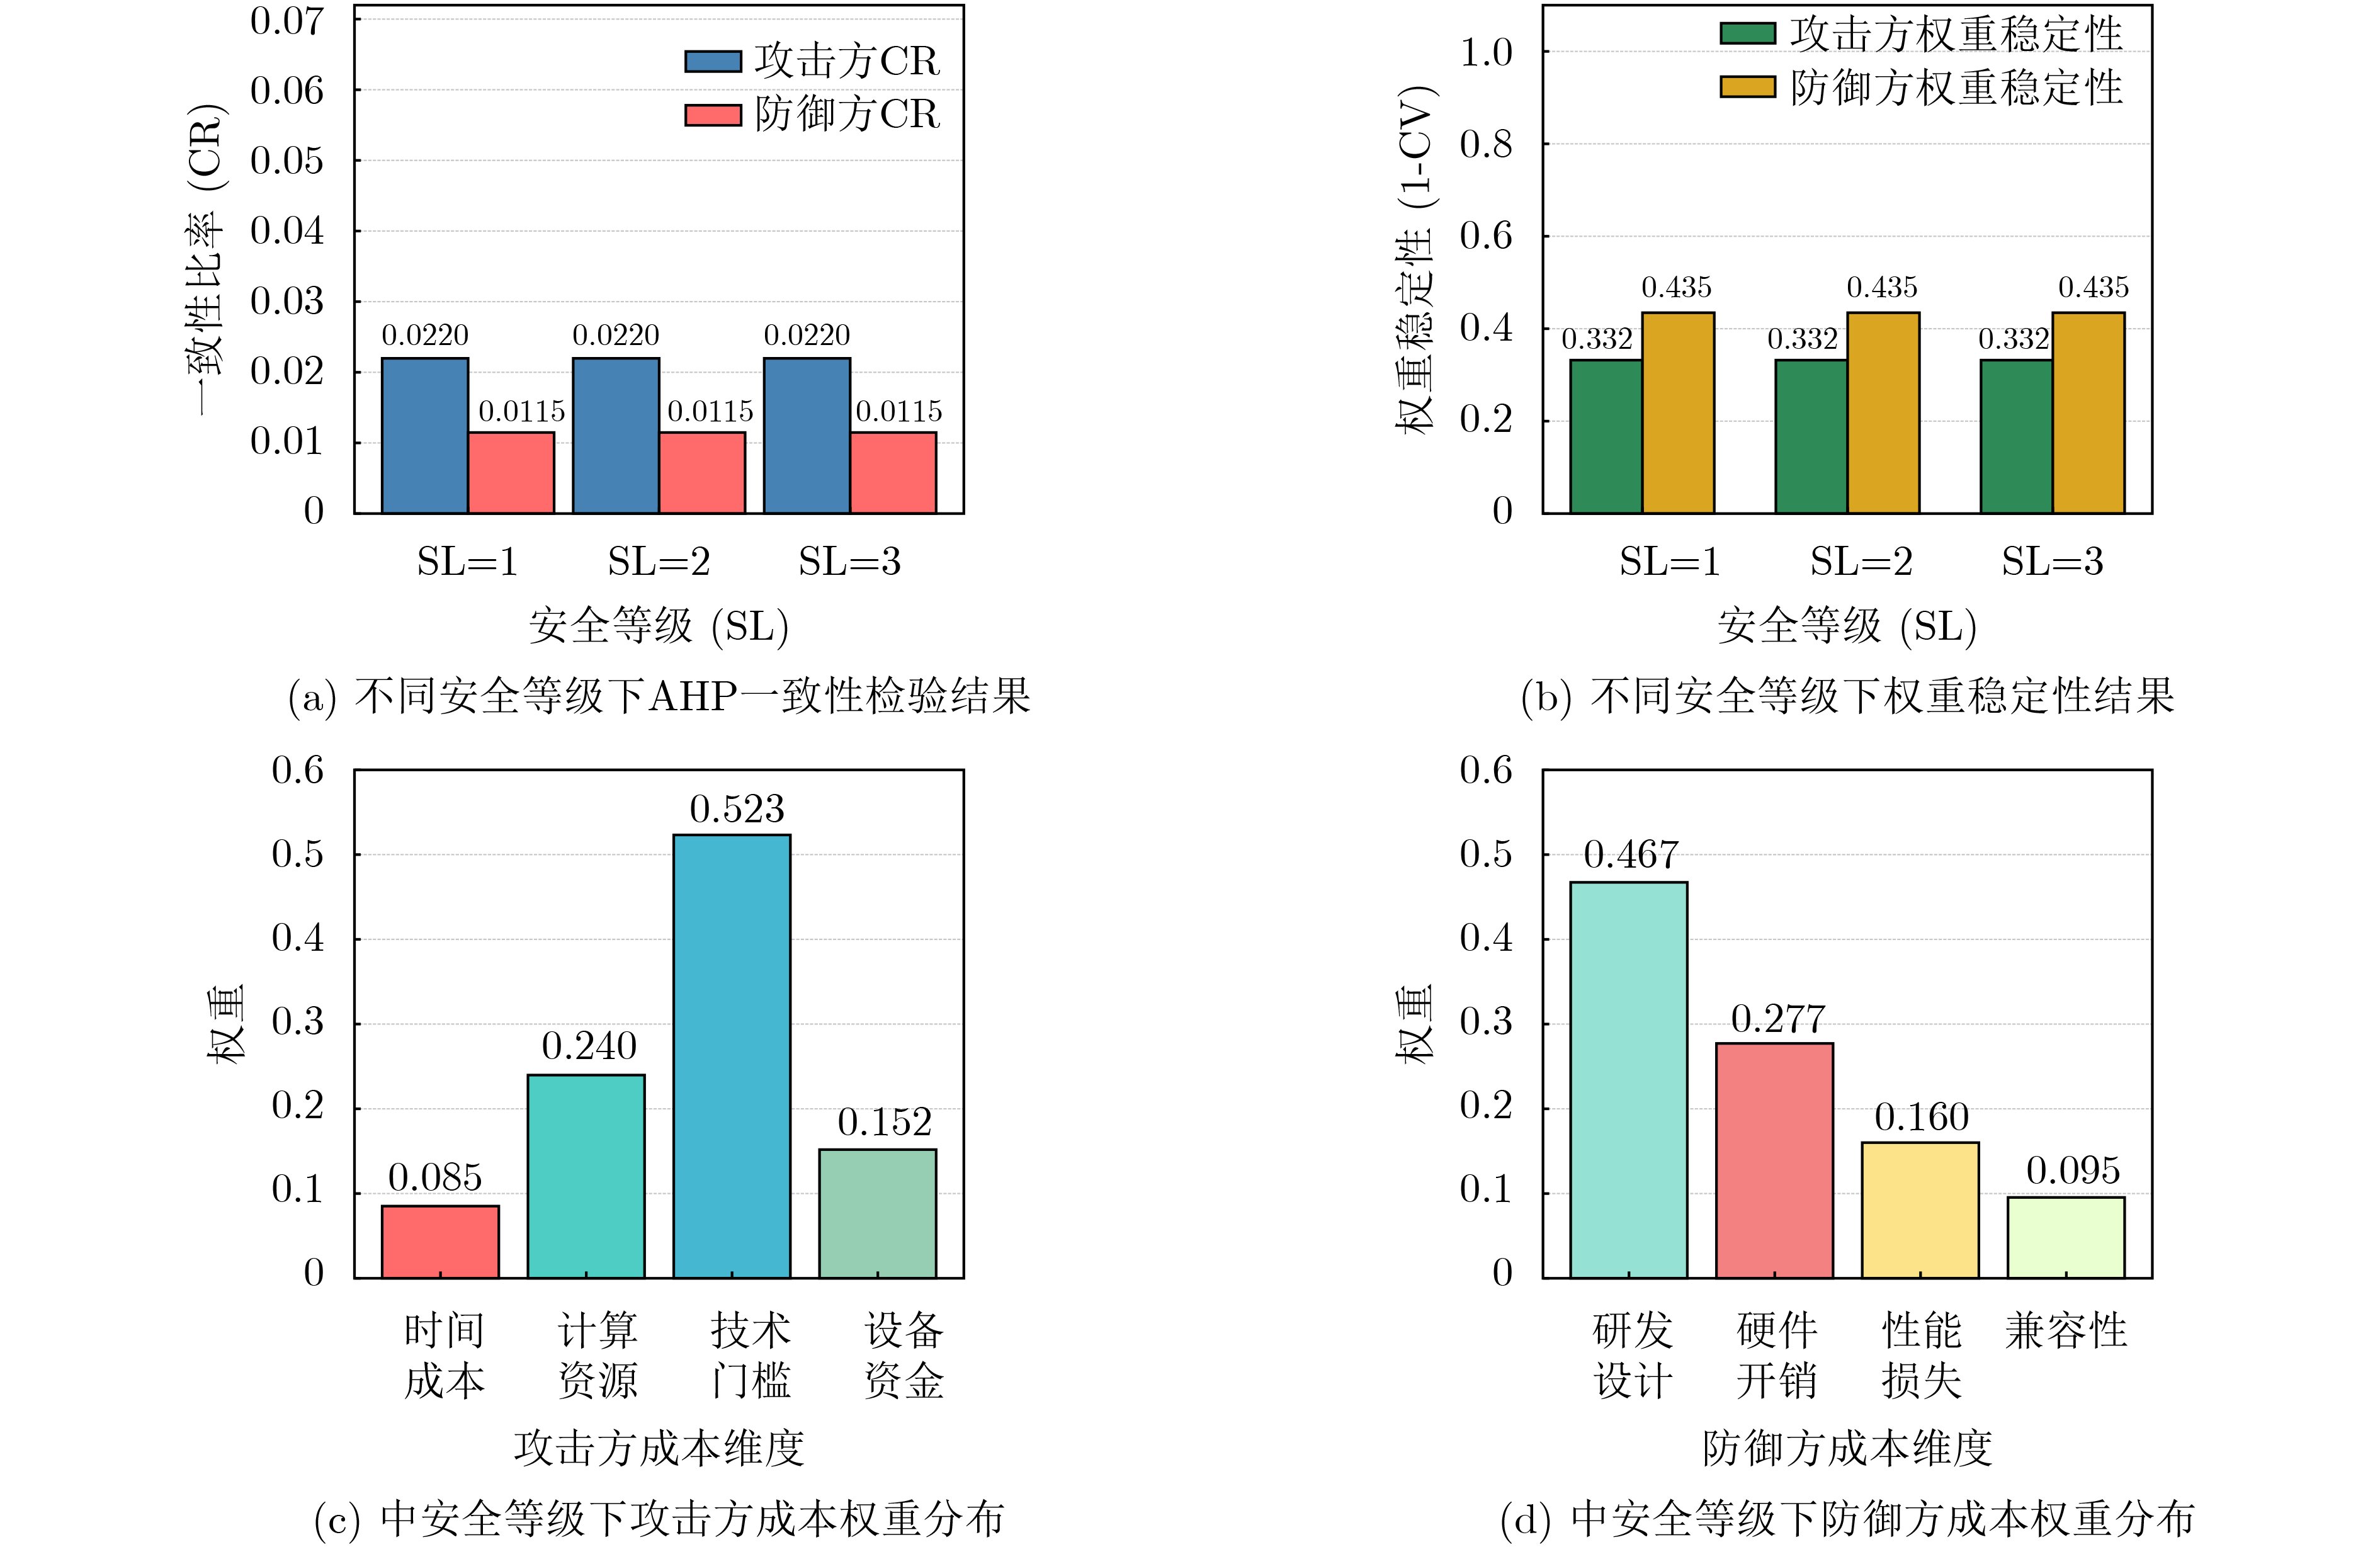
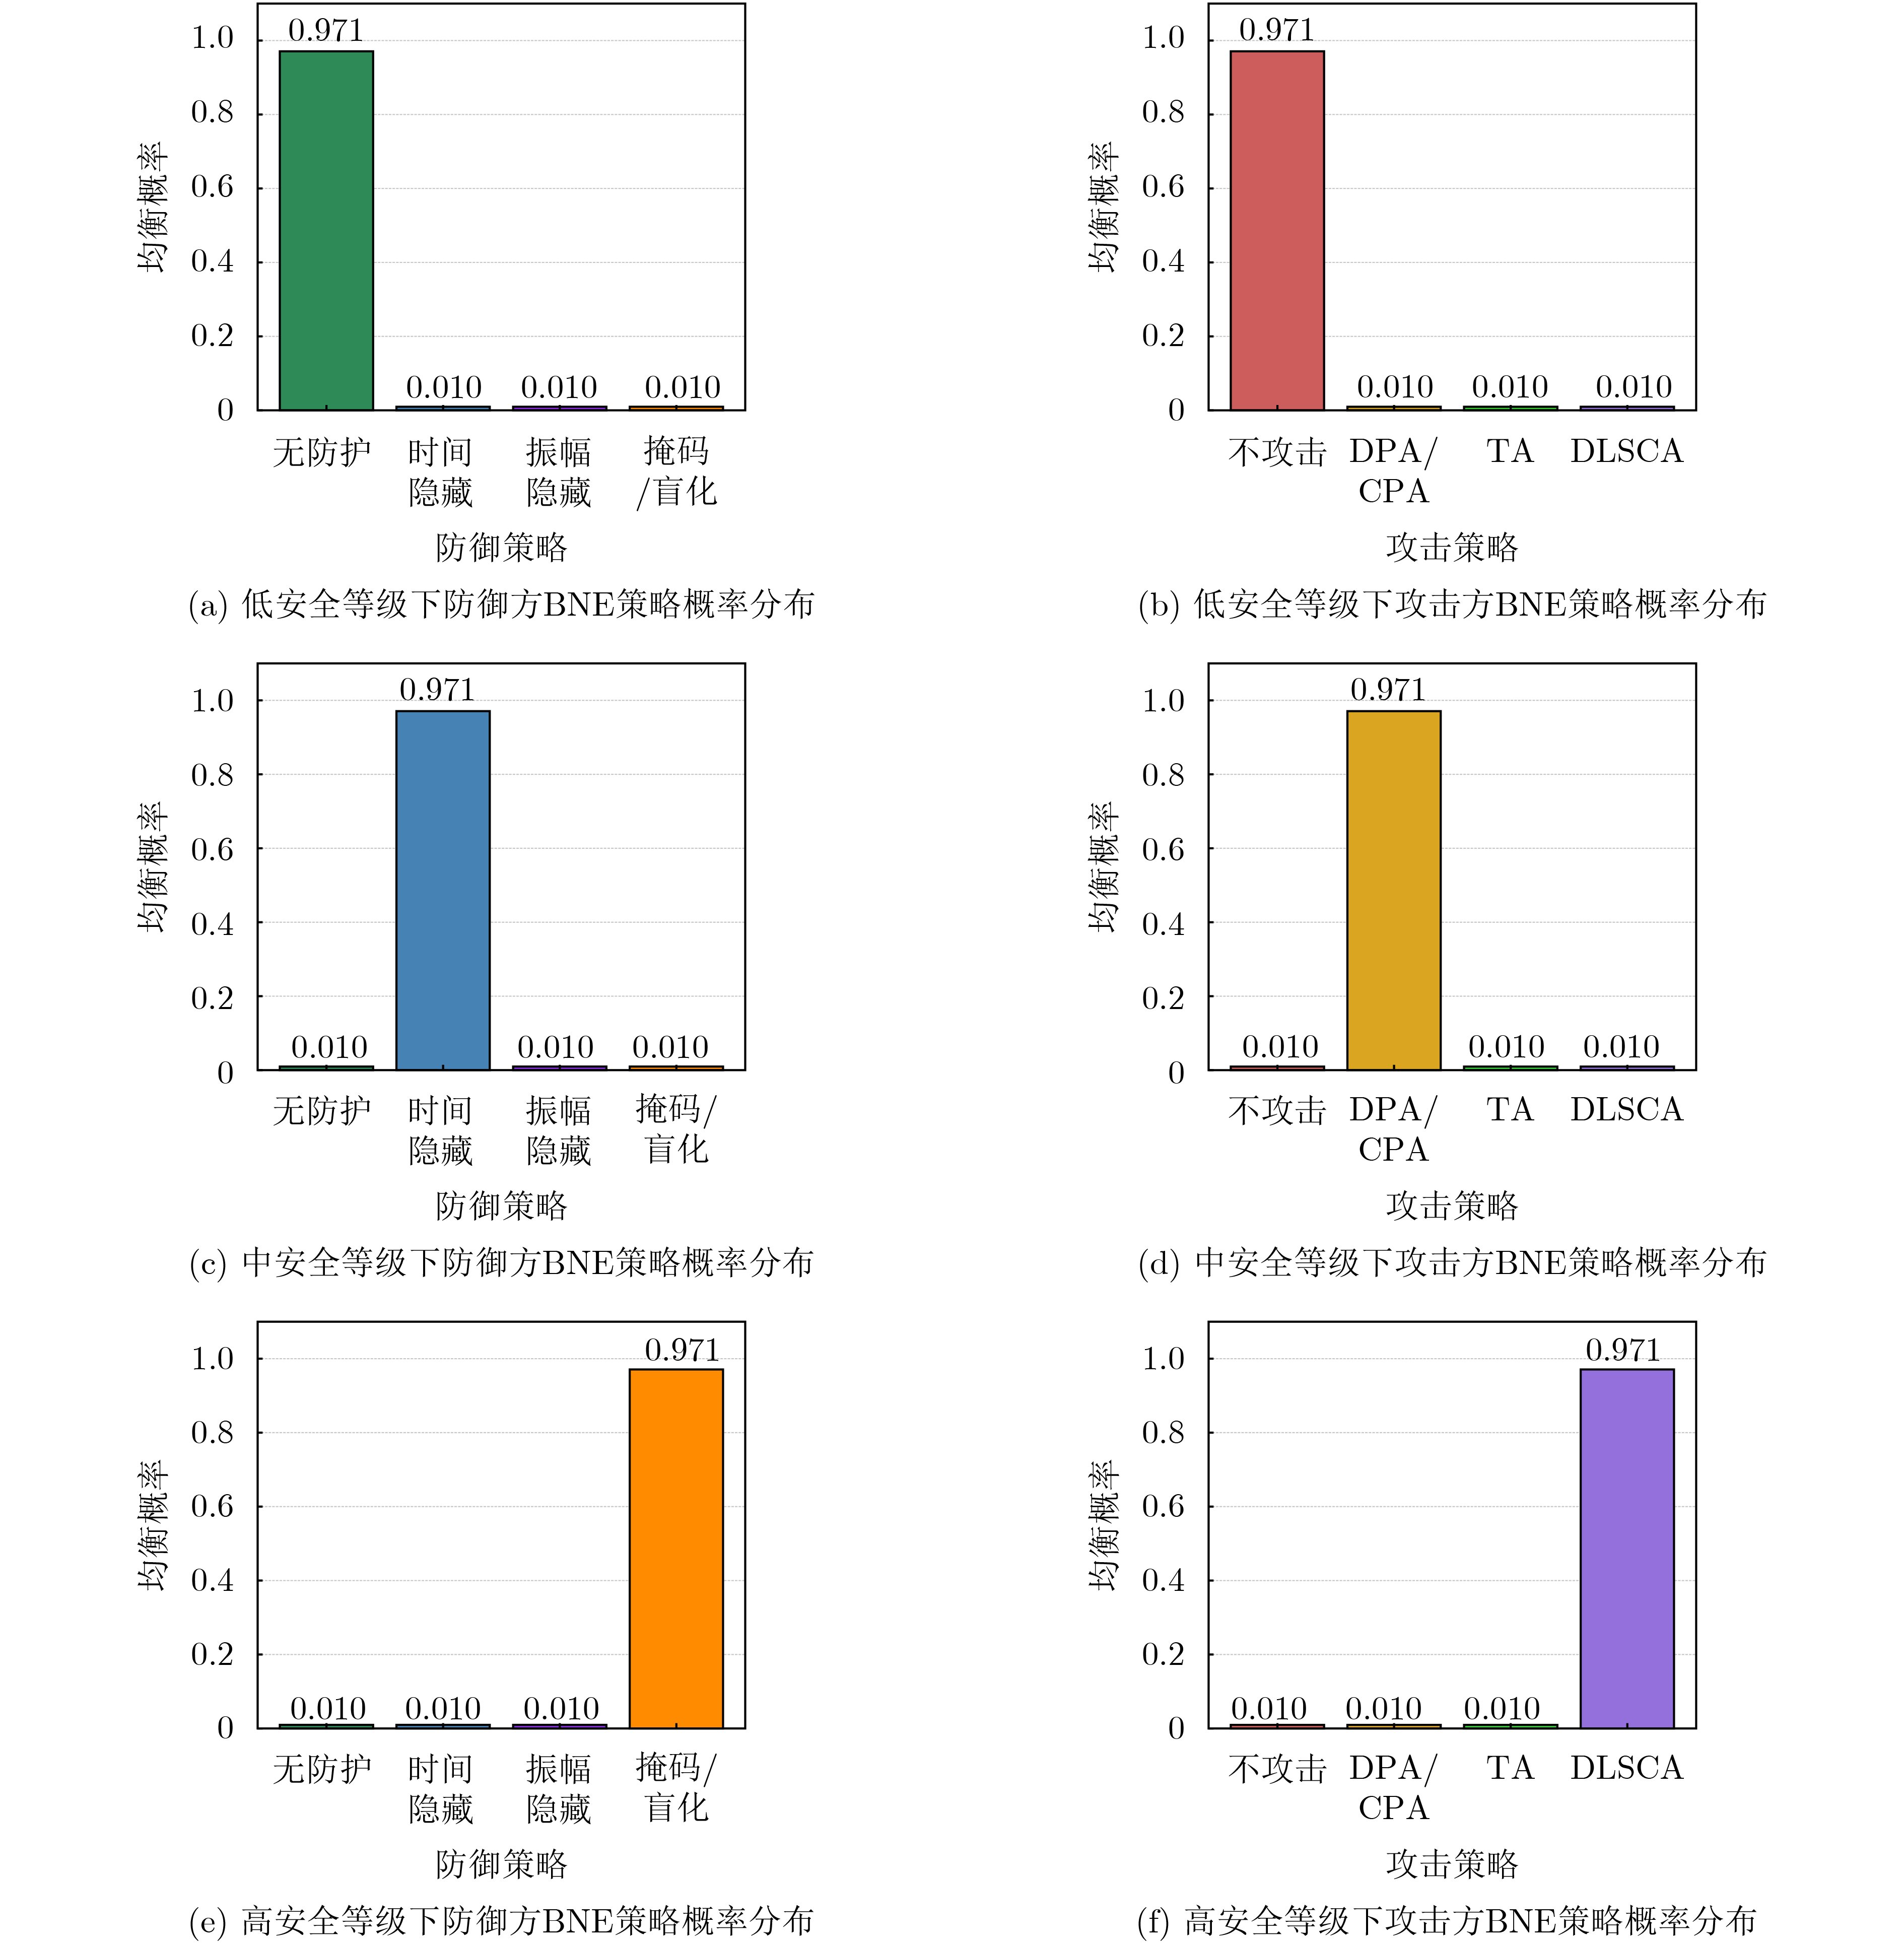
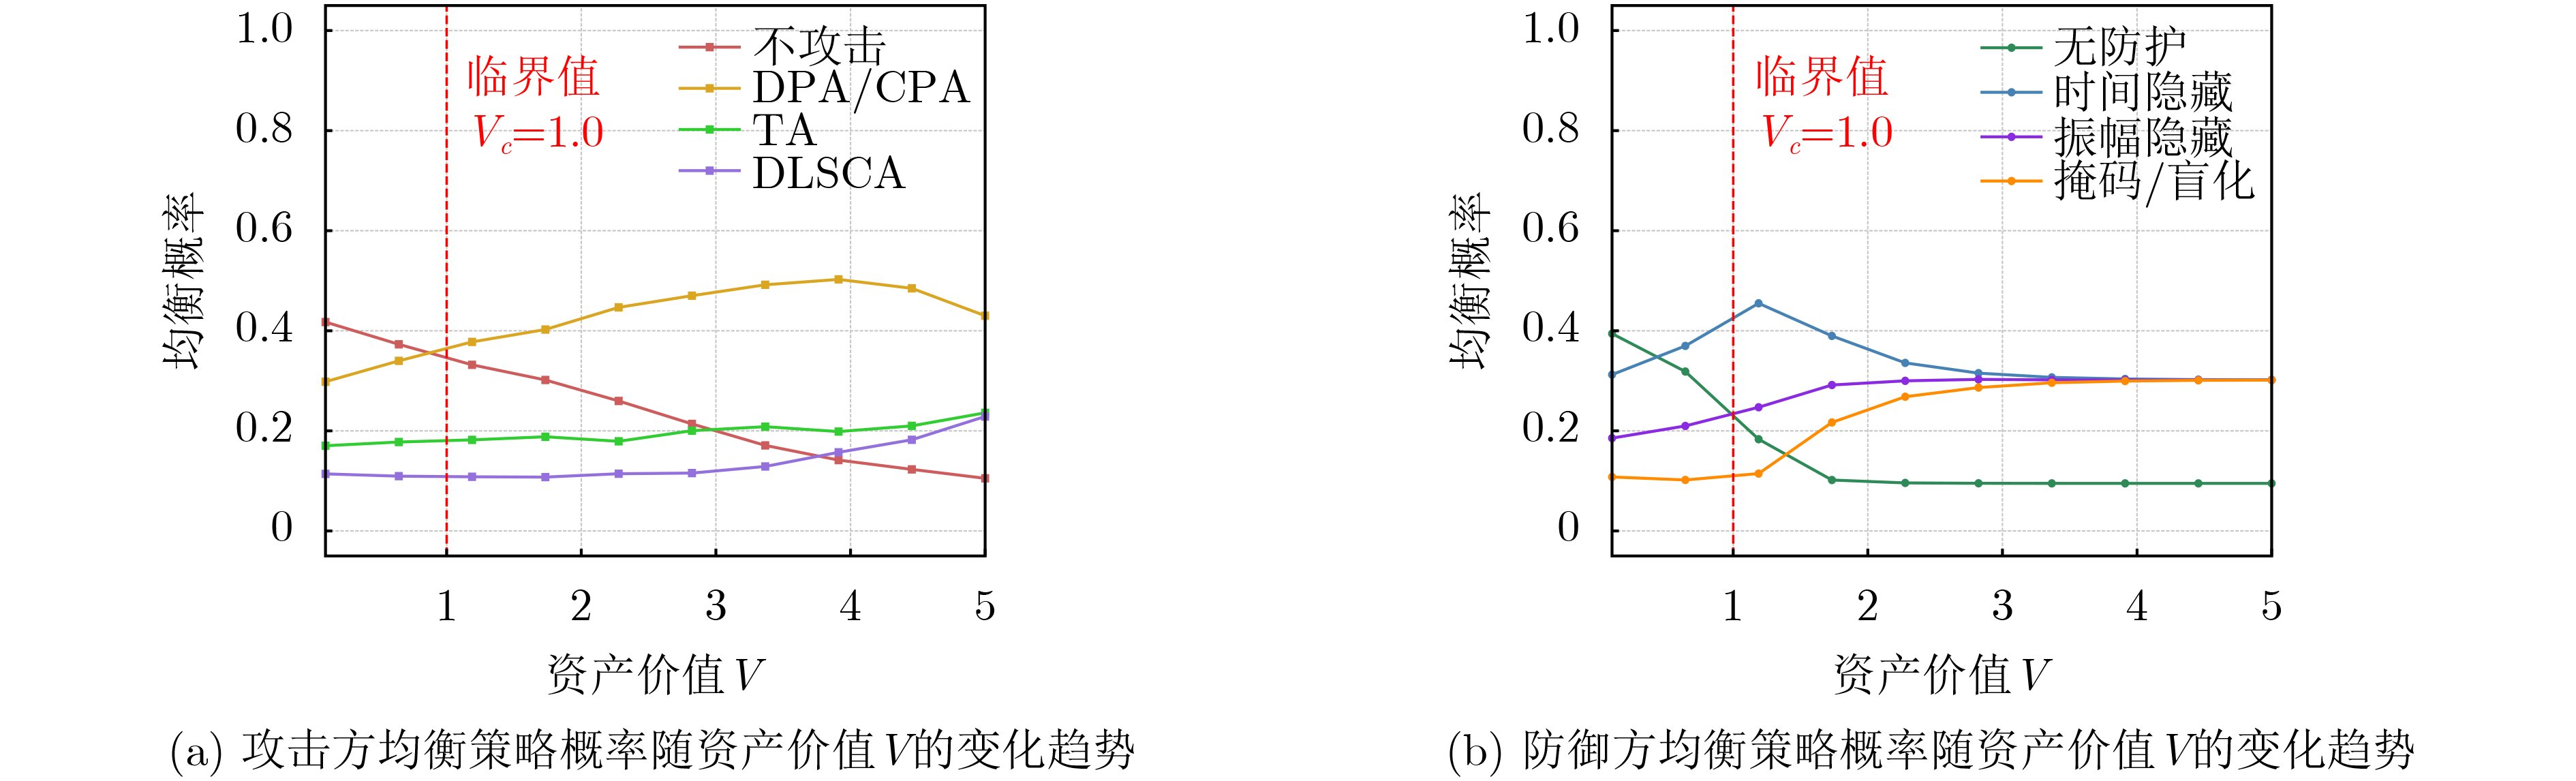
Objective The field of side-channel security lacks a systematic, quantifiable, and reproducible model for selecting attack and defense strategies, particularly in engineering applications where limited resources require informed cost-benefit trade-offs. The absence of such a framework hinders the practical implementation of the principle of appropriate security and often leads to either excessive or insufficient protection of cryptographic modules. Conventional approaches to attack and defense cost evaluation rely heavily on subjective expert judgment, making the results difficult to reproduce and compare systematically. This study proposes an interdisciplinary framework that integrates game theory, behavioral economics, and the Analytic Hierarchy Process (AHP) to establish a structured decision framework. The proposed framework performs structured cost quantification for side-channel attack and defense strategies while incorporating behavioral factors into decision-making under uncertainty, thereby supporting adaptive strategy selection according to asset value and security level. Methods A multilayer modeling framework is developed based on a static game with incomplete information. The side-channel analyst and defense designer are modeled as rational players with finite strategy sets. The attacker selects from Differential Power Analysis/Correlation Power Analysis (DPA/CPA), Template Attack (TA), and Deep Learning-Based Side-Channel Analysis (DLSCA), whereas the defender selects time hiding, amplitude hiding, or masking/blinding countermeasures. An AHP-based structured cost quantification framework is established to quantify strategy costs. Pairwise comparison matrices are used to decompose costs into multiple criteria, including time, data storage, computational resources, expertise, and hardware overhead, and to calculate objective criterion weights, replacing subjective cost assignment with a reproducible hierarchical evaluation framework. To capture realistic decision-making behavior, Prospect Theory and risk-aversion theory are incorporated into the utility function. Behavioral parameters are parameterized by security level, enabling adaptive strategy selection under different security requirements. The resulting behaviorally enhanced Bayesian game is solved using Bayesian Nash Equilibrium (BNE), in which each player’s optimal mixed strategy is determined according to its private type and prior beliefs about the opponent. To satisfy engineering requirements, the As Low As Reasonably Practicable (ALARP) principle is incorporated as an engineering cost-effectiveness constraint, ensuring that selected defense strategies achieve appropriate risk reduction at acceptable cost. Numerical optimization is performed using a customized sequential quadratic programming algorithm implemented in Python. Results and Discussions Comprehensive experiments are conducted to evaluate the consistency, sensitivity, and practical applicability of the proposed framework. The AHP-based structured cost quantification framework demonstrates good internal consistency, with all consistency ratios below the threshold of 0.1, confirming the reliability of the judgment matrices. The resulting weight distributions indicate that attackers assign greater importance to technical barriers and computational resources, whereas defenders place greater emphasis on design complexity and performance overhead. The behavioral adjustment mechanism effectively modifies subjective cost according to security level. Under low-security conditions, stronger risk aversion increases perceived cost and promotes conservative strategy selection. Under high-security conditions, decision-making becomes more consistent with objectively quantified costs. Equilibrium analysis under different asset values and security levels produces interpretable strategy distributions. For low-value assets, both players tend to select low-cost or no-action strategies that satisfy the lower boundary of the ALARP acceptable region. As asset value increases, a clear threshold effect drives both players toward higher-cost, higher-effectiveness strategies, including DLSCA and masking/blinding techniques. Sensitivity analysis further demonstrates that the probability of adopting stronger defense strategies increases monotonically with asset value, confirming the framework’s ability to characterize the nonlinear relationship between protection intensity and asset value. These results demonstrate that the proposed framework supports adaptive, context-aware security decision-making by jointly considering structured cost, risk, and behavioral factors. Conclusions This study proposes a behaviorally informed game-theoretic framework for selecting side-channel attack and defense strategies, addressing the lack of a systematic approach to structured cost quantification in existing studies. By integrating AHP-based structured cost quantification, behaviorally adjusted subjective cost, and ALARP-based engineering cost-effectiveness constraints, the proposed framework provides a reproducible, multidimensional, and context-dependent approach to analyzing attack and defense strategies. The framework explicitly associates security level with behavioral parameters, enabling dynamic strategy selection according to both asset value and decision-makers’ risk preferences. Although the current implementation relies partly on expert-defined parameters and adopts a static game framework, it establishes a quantitative foundation for replacing heuristic security decisions with interdisciplinary, data-driven analysis. Future work will focus on calibrating model parameters using practical side-channel attack and defense datasets, extending the framework to multistage dynamic games to characterize long-term strategic evolution, and validating the framework in practical cryptographic security evaluation scenarios. The proposed framework provides the first systematic methodology for cost-aware and behaviorally informed optimization of side-channel attack and defense strategies, offering both theoretical support and practical guidance for achieving appropriate security in cryptographic engineering. -
1 行为增强的贝叶斯-纳什均衡求解算法
输入:资产价值$ V $,安全等级$ \text{SL} $,成本矩阵$ \mathbf{C} $,成功率矩阵P,信念分布$ \{{\beta }_{{\mathrm{A}}},{\beta }_{{\mathrm{D}}}\} $ 输出:均衡策略$ (\sigma _{\rm A}^{*},\sigma _{\rm D}^{*}) $ (1) 确定行为参数:$ {\alpha }_{\rm D}(\text{SL}),{\alpha }_{\rm A}(\text{SL}),{\lambda }_{\rm D}(\text{SL}),{\lambda }_{\rm A}(\text{SL}),{R}_{0,{\mathrm{D}}},{R}_{0,{\mathrm{A}}} $; (2) 计算调整后成本:$ {\mathbf{C}}^{\prime}\leftarrow \text{AdjustCost}(\mathbf{C},\text{SL},V) $ //式(15) (3) 计算风险调整收益:$ {U}^{\text{risk}}\leftarrow \text{RiskAdjust}(\mathbf{P},V,{\mathbf{C}}^{\prime},{\alpha }_{\rm D},{\alpha }_{\rm A}) $ (4) 应用前景理论调整:$ {U}^{\text{PT}}\leftarrow \text{ProspectAdjust}({U}^{\text{risk}},{\lambda }_{\rm D},{\lambda }_{\rm A},{R}_{0,D},{R}_{0,A}) $ (5) 应用ALARP约束:$ {S}_{\text{feasible}}\leftarrow \text{ALARPFiliter}({U}^{\text{PT}},{\mathbf{C}}^{\prime},V,{\varTheta }^{\text{ALARP}}) $ (6) 构建优化问题: (7) 目标函数:$ {\max }_{{{\sigma }_{\rm D}},{{\sigma }_{\rm A}}}\left(\displaystyle\sum \nolimits_{{s}_{d}}{\sigma }_{\rm D}({s}_{d})\cdot {\text{EU}}_{\rm D}({s}_{d})+\displaystyle\sum \nolimits_{{s}_{a}}{\sigma }_{\rm A}({s}_{a})\cdot {\text{EU}}_{\rm A}({s}_{a})\right) $ (8) 约束条件:$ \sum {\sigma }_{\rm D}=1, \sum {\sigma }_{\rm A}=1, {\sigma }_{i}\geq 0, {s}_{i}\in {S}_{\text{feasible}} $ (9) 使用SLSQP算法求解上述优化问题; (10) 验证BNE条件:检查是否满足式(27)和式(28); (11) If 验证失败 then (12) 调整初始点,重新执行步骤(7)~(9)求解优化问题; (13) end (14) return $ (\sigma _{\rm A}^{*},\sigma _{\rm D}^{*}) $;  下载: 导出CSV
表 1 攻击成功率矩阵$ {{\boldsymbol{P}}}_{{\mathrm{A}}}({s}_{a},{s}_{d}) $
pA\防御策略 A(无防护) B(时间隐藏) C(振幅隐藏) D(掩码/盲化) a(不攻击) 0.00 0.00 0.00 0.00 b(DPA/CPA) 0.60 0.40 0.10 0.20 c(TA) 0.80 0.10 0.25 0.30 d(DLSCA) 0.90 0.30 0.35 0.50
下载: 导出CSV
表 2 安全等级依赖的行为参数设定
安全等级 风险规避系数$ \alpha $ 损失厌恶系数$ \lambda $ ALARP边界$ [{\theta }_{\min },{\theta }_{\max }] $ $ \rho $ 参考点$ {R}_{0} $ SL=1 1.50(攻) 1.20(防) 2.50(攻) 2.00(防) [0.05, 0.10](攻) [0.10, 0.20](防) 1.20 0 SL=2 0.80(攻) 0.60(防) 1.80(攻) 1.50(防) [0.10, 0.30](攻) [0.15, 0.40](攻) 1.00 0 SL=3 0.30(攻) 0.20(防) 1.20(攻) 1.00(防) [0.30, 0.80](攻) [0.25, 0.60](攻) 0.80 0
下载: 导出CSV
-
[1] KOCHER P, JAFFE J, and JUN B. Differential power analysis[C]. 19th Annual International Cryptology Conference on Advances in Cryptology, Santa Barbara, USA, 1999: 388–397. doi: 10.1007/3-540-48405-1_25. [2] QUISQUATER J J and SAMYDE D. ElectroMagnetic analysis (EMA): Measures and counter-measures for smart cards[C]. Smart Card Programming and Security International Conference on Research in Smart Cards, Cannes, France, 2001: 200–210. doi: 10.1007/3-540-45418-7_17. [3] KOCHER P C. Timing attacks on implementations of Diffie-Hellman, RSA, DSS, and other systems[C]. 16th Annual International Cryptology Conference on Advances in Cryptology, Santa Barbara, USA, 1996: 104–113. doi: 10.1007/3-540-68697-5_9. [4] ISO. ISO/IEC 17825: 2024 Information technology—security techniques—testing methods for the mitigation of non-invasive attack classes against cryptographic modules[S]. Geneva: ISO, 2024. [5] YD/T 6305.2024 安全芯片非入侵式攻击缓解测试方法 [S]. 北京: 邮电部标准出版社, 2024. [6] 姚剑波, 张涛. 基于互信息博弈的侧信道攻击安全风险评估[J]. 计算机科学, 2012, 39(S1): 69–71.YAO Jianbo and ZHANG Tao. Side channel risk evaluation based on mutual information game[J]. Computer Science, 2012, 39(S1): 69–71. [7] WANG Bing, LOU Wenjing, and HOU Y T. Modeling the side-channel attacks in data deduplication with game theory[C]. 2015 IEEE Conference on Communications and Network Security (CNS), Florence, Italy, 2015: 200–208. doi: 10.1109/CNS.2015.7346829. [8] GENG Hui, KWIAT K A, KAMHOUA C A, et al. On random dynamic voltage scaling for internet-of-things: A game-theoretic approach[J]. IEEE Transactions on Computer-Aided Design of Integrated Circuits and Systems, 2018, 37(1): 123–132. doi: 10.1109/TCAD.2017.2717780. [9] HALPERN J and TEAGUE V. Rational secret sharing and multiparty computation: Extended abstract[C]. Proceedings of the Thirty-sixth Annual ACM Symposium on Theory of Computing, Chicago, USA, 2004: 623–632. doi: 10.1145/1007352.1007447. [10] 彭长根, 田有亮, 刘海, 等. 密码学与博弈论的交叉研究综述[J]. 密码学报, 2017, 4(1): 1–15. doi: 10.13868/j.cnki.jcr.000158.PENG Changgen, TIAN Youliang, LIU Hai, et al. A survey on the intersection of cryptography and game theory[J]. Journal of Cryptologic Research, 2017, 4(1): 1–15. doi: 10.13868/j.cnki.jcr.000158. [11] 刘小虎, 张恒巍, 张玉臣, 等. 基于博弈论的网络攻防行为建模与态势演化分析[J]. 电子与信息学报, 2021, 43(12): 3629–3638. doi: 10.11999/JEIT200628.LIU Xiaohu, ZHANG Hengwei, ZHANG Yuchen, et al. Modeling of network attack and defense behavior and analysis of situation evolution based on game theory[J]. Journal of Electronics & Information Technology, 2021, 43(12): 3629–3638. doi: 10.11999/JEIT200628. [12] SUN Haiyan, SHAO Chenglong, ZHANG Jianwei, et al. Evolution analysis of network attack and defense situation based on game theory[J]. Computers, Materials and Continua, 2025, 83(1): 1451–1470. doi: 10.32604/cmc.2025.059724. [13] BAI Xue and BAI Yongguo. Equilibrium strategy of attack and defense in computer networks based on Markov signal game theory[J]. Journal of Cyber Security and Mobility, 2025, 14(1): 127–153. doi: 10.13052/jcsm2245-1439.1416. [14] ZHENG Tianshuai, DU Ye, HUA Kaisheng, et al. Predictive analytics for cyber-attack timing in power Internet of Things: A FlipIt game-theoretic approach[J]. Internet of Things, 2025, 30: 101522. doi: 10.1016/j.iot.2025.101522. [15] ZHU Zinan and ZHOU Lin. Application of complex network attack and defense time game model in network security defense decision[J]. Journal of Cyber Security and Mobility, 2025, 14(2): 311–337. doi: 10.13052/jcsm2245-1439.1423. [16] HE Long, SUN Geng, NIYATO D, et al. Generative AI for game theory-based mobile networking[J]. IEEE Wireless Communications, 2025, 32(1): 122–130. doi: 10.1109/MWC.007.2400133. [17] MAO Shaoguang, CAI Yuzhe, XIA Yan, et al. ALYMPICS: LLM agents meet game theory[C]. Proceedings of the 31st International Conference on Computational Linguistics, Abu Dhabi, UAE, 2025: 2845–2866. [18] TARIQ A, SALLABI F, SERHANI M A, et al. Leveraging game theory and XAI for data quality-driven sample and client selection in trustworthy split federated learning[J]. IEEE Transactions on Consumer Electronics, 2025, 71(2): 6686–6699. doi: 10.1109/TCE.2025.3543209. [19] PIRHOSSEINI H, ZAREI E, REZVANI M H, et al. Game-theoretic methods for edge/fog/cloud computation offloading: A systematic review[J]. Computing, 2025, 107(8): 166. doi: 10.1007/s00607-025-01515-x. [20] 张鸿, 廖彧歆, 王汝言, 等. 面向密集场景的空天地网络资源分配算法[J]. 电子与信息学报, 2024, 46(5): 1968–1976. doi: 10.11999/JEIT231086.ZHANG Hong, LIAO Yuxin, WANG Ruyan, et al. Resource allocation algorithm of space-air-ground integrated network for dense scenarios[J]. Journal of Electronics & Information Technology, 2024, 46(5): 1968–1976. doi: 10.11999/JEIT231086. [21] 冯·诺伊曼, 摩根斯特恩, 王文玉, 王宇, 译. 博弈论与经济行为[M]. 北京: 三联书店, 2004.VON NEUMANN J, MORGENSTERN O, WANG Wenyu, WANG Yu, translation. Theory of Games and Economic Behavior[M]. Beijing: SDX Joint Publishing Company, 2004. [22] SAATY T L. A scaling method for priorities in hierarchical structures[J]. Journal of Mathematical Psychology, 1977, 15(3): 234–281. doi: 10.1016/0022-2496(77)90033-5. [23] SAATY R W. The analytic hierarchy process—what it is and how it is used[J]. Mathematical Modelling, 1987, 9(3/5): 161–176. doi: 10.1016/0270-0255(87)90473-8. [24] KAHNEMAN D and TVERSKY A. Prospect theory: An analysis of decision under risk[M]. MacLean L C and Ziemba W T. World Scientific Handbook in Financial Economics Series: Handbook of the Fundamentals of Financial Decision Making, 2013: 99–127. doi: 10.1142/9789814417358_0006. [25] OŻGA S A. Aspects of the theory of risk-bearing[J]. Economica, 1966, 33(130): 251–252. doi: 10.2307/2552628. [26] 国家密码管理局. GM/T 0083-2020 密码模块非入侵式攻击缓解技术指南[S]. 北京: 中国标准出版社, 2021.State Cryptography Administration. GM/T 0083-2020 Guideline for the mitigation of non-invasive attacks against cryptographic modules[S]. Beijing: Standards Press of China, 2021. -

 下载:

图(5) / 表(3)
计量
- 文章访问数: 446
- HTML全文浏览量: 195
- PDF下载量: 34
- 被引次数: 0
